Professionally Evil Testing as a Service (PETaaS®)
Partnership-Based Security Testing.
Your Schedule. Your Priorities.
Exclusively from Secure Ideas.
Custom-Fit Expertise for Every Engagement
Prepay for expert-led testing capacity, then spend it on the work you need, when you need it.
Professionally Evil Testing as a Service (PETaaS®) is a prepaid credit program. One credit equals one eight-hour consultant day at our standard rate of $2,720. You purchase credits up front and apply them to any effort-based Secure Ideas service, including penetration testing, security assessments, architecture reviews, tabletop exercises and training.
Security programs do not run on a fixed schedule. New applications launch, compliance deadlines move, and incidents change priorities. Credits let you respond to those changes without renegotiating scope or signing a new contract for every engagement.
The larger your commitment, the larger your discount.
Built-in advisory services mean your team has direct access to our consultants via Slack, email, and video calls for guidance between tests on security policy and procedures. We also offer monthly reporting keeps leadership informed with roll-up metrics, credit usage, and strategic recommendations.
Fill out the form to get started.

How Can We Help You?
From Procurement to Testing, Without the Friction
THE CREDITS SYSTEM
Buy Once. Deploy Against Whatever Comes Up.
PETaaS® replaces the traditional “scope a project, get a quote, sign a contract, wait for scheduling” cycle with something far more practical. Buy credits upfront, then deploy them against whatever testing needs arise throughout the year.
Need a web application test before a release? Use credits. Want to assess a new API? Use credits. Discovered a concern during an advisory call and want to dig deeper? Use credits. No new statements of work, no procurement delays, no wasted time.
You can use credits for:
Web Application Testing
Pre-release assessments, full app reviews, feature-level testing
Network Penetration Testing
Internal and external network assessments
API Assessments
REST, GraphQL, and custom API security testing
Cloud Security
AWS, Azure, GCP configuration and access reviews
Mobile Application Testing
iOS and Android application security assessments
John Polson
Senior Information Security Auditor
Comprehensive, Manual Reporting
We allocate sufficient time within each engagement for thorough documentation, ensuring you receive clear explanations of discovered vulnerabilities, proof-of-concept details, and practical remediation guidance.
All of our penetration tests include dedicated time for report creation and peer review. Our testers don’t use automated templates or generic outputs, each report is manually written specifically for your environment and findings. You get a report that accurately reflects your unique environment, written by the same testers who conducted the assessment.
This isn’t an afterthought; it’s a core part of how we deliver value.
WHO PETAAS® IS FOR
Built for Teams That Take Security Seriously
PETaaS® works best for organizations that have outgrown one-off engagements and need a testing partner who understands their environment over time.
Security Leaders
“I need continuous testing, but I can’t keep running procurement for every engagement.”
Your Needs: Your compliance requirements are evolving, your board wants evidence of ongoing security validation, and spinning up a new vendor contract every quarter is eating your time.
PETaaS® gives you: One procurement cycle, credits you deploy on your schedule, monthly reporting for leadership, and a dedicated team that already knows your environment.
Engineering & DevOps Teams
“We ship fast and need testing that keeps up with our specific release cycle.”
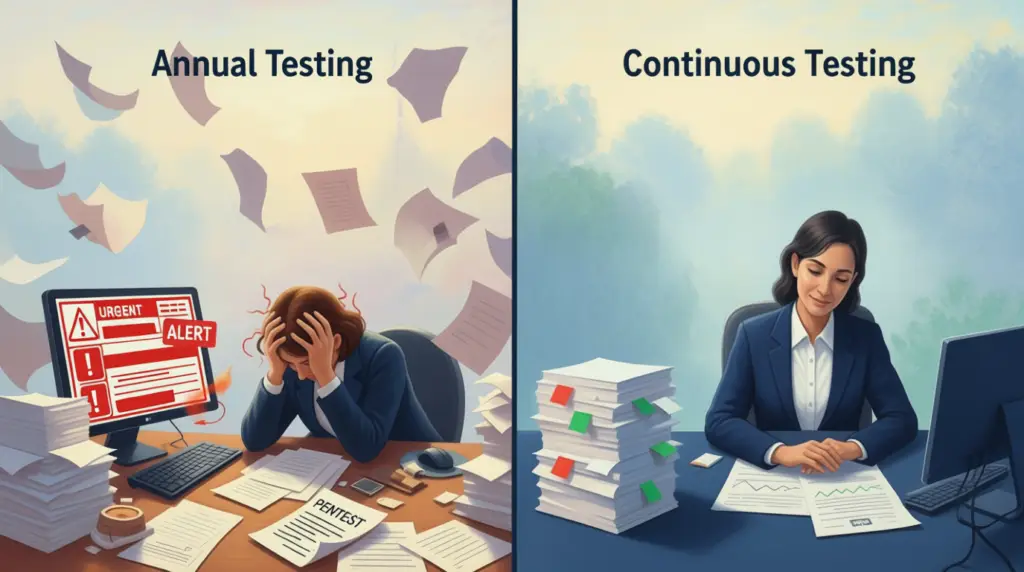
Your Needs: Annual pentests happen months after features go live. By the time findings come back, the codebase has moved on and remediation means rework across multiple sprints.
PETaaS® gives you: Credits allocated per epic or release, testing embedded into your SDLC, and real-time findings via Slack so your team can fix issues before they reach production.
Compliance & Risk Experts
“Our auditor wants evidence of continuous security validation, not just an annual report.”
Your Needs: PCI DSS 4.0, GLBA, and HIPAA are all moving toward continuous testing expectations. A single pentest report from nine months ago is not going to satisfy your QSA or examiner.
PETaaS® gives you: Monthly testing cadence, documented findings with remediation tracking, advisory support for interpreting regulatory requirements, and reporting that auditors trust.
Built for Security Leaders Who Demand More
Volume Discounts
We pass savings on to you as we learn more about your environment and technologies.
Less administrative overhead means better pricing.
30 – 44 Credits
$77,520 – $113,696
45 – 59 Credits
$110,160 – $144,432
60 – 89 Credits
$138,720 – $205,768
90+ Credits
$195,840+
Credits are valid for 2 years from purchase date.
Credits are non-refundable and spent in whole-number increments only.
How Many Credits Will You Need?
Every engagement is scoped individually, but we have found these are the typical ranges, provided here to help with budgeting.
Credit estimates include all testing, analysis, and reporting.
Network Pentesting
Web App Pentesting
Other Services
These are typical ranges based on years of experience. Actual effort is determined through a detailed scoping exercise with your team before any engagement begins.
PETaaS®
Frequently
Asked
Questions
Have a question that isn’t answered here?
See our full FAQ page.
What is Professionally Evil Testing as a Service (PETaaS®)?
PETaaS® is on-demand pentesting services, which provides you with continuous access to our penetration testing expertise rather than a one-time assessment. This approach offers on-demand or scheduled testing, which integrates with your software development lifecycle, and delivers regular vulnerability analysis with ongoing support. While it may initially appear more expensive than traditional testing, PETaaS® is significantly more cost-effective than hiring full-time security staff and provides proactive, real-time vulnerability identification.
Note: The industry lacks a standard definition for penetration testing as a service, so verify that your provider’s approach aligns with your expectations.
What is a PETaaS® credit?
One credit equals one eight-hour consultant day at our standard day rate of $2,720. Credits can be applied toward any effort-based Secure Ideas service, including penetration testing, security assessments, tabletop exercises, and more.
How is a credit priced?
One credit is priced at our standard day rate of $2,720. Volume discounts of 5% to 20% apply based on the number of credits purchased.
Can I switch between flat fee and credits?
Yes. You can move between service models during the contract by purchasing the difference in credits.
How do I schedule a test with credits?
How long are credits valid?
Credits are valid for two years from the start of the contract.
What types of testing can I use credits for?
Credits can be applied to any testing type Secure Ideas offers, including web application penetration testing, network penetration testing, API assessments, cloud security assessments, mobile application testing, and more. Your advisory team can help determine the right allocation for your needs.
What does advisory access include?
Advisory access provides direct communication with Secure Ideas consultants through Slack, email, video calls, and our portal. You can ask security questions, get guidance on technology decisions, discuss findings from previous tests, and receive support navigating compliance requirements. Most inquiries receive same-day responses.
How is PETaaS® different from automated PTaaS platforms?
Automated platforms run scanners on a schedule and present the results. PETaaS® delivers manual testing performed by experienced human consultants who understand attack paths, business context, and how vulnerabilities chain together. We identify how attackers actually compromise environments, not just which CVEs are present.
Does PETaaS® meet PCI DSS 4.0 continuous testing requirements?
Yes. PETaaS® was designed with evolving compliance requirements in mind, including PCI DSS 4.0’s shift toward continuous security validation. Our Continuous Penetration Testing tier provides monthly testing over 12 months, delivering the ongoing human-led validation and documentation that QSAs expect.
Can PETaaS® integrate into our SDLC?
Absolutely. Credits can be allocated to test features within specific epics or releases, allowing you to embed real penetration testing into your development workflow. This catches vulnerabilities before they reach production, reducing the cost and risk of post-deployment remediation.
Can we see a sample report from a Penetration Test?
Absolutely. Any reputable penetration testing company should provide sample reports upon request. Reports are your primary deliverable and should include an executive summary, testing narrative, detailed findings with risk ratings, replication steps for verification, and actionable remediation recommendations. Not all reports are created equal, so reviewing samples helps ensure the format and content meet your needs. Most companies will accommodate reasonable modifications to reporting formats.
Recognized authority and trusted guidance built on years of uncovering risks for organizations like yours.
Five… Four… Three… Two… One…
Satellite systems, ground stations, communication paths. Our CEO Kevin Tackett breaks down a holistic framework for testing complex environments that most people assume are “secure by obscurity.” If your attack surface extends beyond traditional IT, this one’s for you.