
Physical Testing
Locks Are Only Secure When They’re Used
Your Weakest Control Might Be a Held Door
Through physical penetration testing and social engineering, you find out whether your badge readers, cameras, and security guards actually stop someone, or whether a uniform and a confident walk get the job done instead. We test reconnaissance, social engineering, RFID cloning, lock bypass, and dumpster diving, the same techniques a real intruder would use to get past your physical controls.
Electronic social engineering testing lets you find out whether your security training and policies are effective by sending test phishing, voice phishing (vishing) and SMS phishing (smishing) campaigns at your teams. We develop pretexts that seem real, and send messages to try and convince people to give us access.
Our testing reveals more than a list of unlocked doors. You’ll understand how an attacker could chain a tailgated entry into network access, which of your staff’s habits create the biggest openings, and how your security culture holds up when someone is actually standing in your lobby. Every finding comes with practical, prioritized recommendations, not just a lecture about vigilance.
Whether you’re validating a recent investment in access control, meeting a compliance requirement, or just want to know if your team would notice, physical testing gives you an honest answer instead of an assumption.
Fill out the form to scope your OT pentest.

Let's Talk About Your Office
Tell us about the spaces you need secured and we’ll be in touch.
Our Penetration Testing Process
Thorough testing with business-focused analysis.
We identify attack paths, evaluate realistic impact to your operations, and provide prioritized guidance that aligns with your resources and goals.

Information Security Officer
Finance
Reconnaissance Through the Front Door
Tailgating and Impersonation
Counterfeit Credentials
Beyond Simple Picking
1 Credit = Up to 1 Full Day of Expert Work
Purchase credits ahead of time, and arrange testing as you need it. Partnership-based security testing on your schedule. One credit gets you up to one full day of expert work from consultants who understand your business. Engage our team as needed with complete flexibility.
Ongoing advisory services included for no extra charge. No rigid scopes, real-time collaboration, and engagement tailored to your priorities.
Exclusively from Secure Ideas.
You Can't Patch a Held Door
Your organization may have strong policies and technical controls, but there are a lot of nooks and crannies that can get overlooked, and some issues are never visible until someone tries to exploit them. A physical penetration test identifies those vulnerabilities the way a real attacker would find them, validates whether your security investments are performing as intended, and helps to meet the compliance requirements your industry demands. It also tests something no policy document can: how your staff, your procedures, and your security culture react when a stranger is standing in your lobby.
Beyond safeguarding data and physical assets, this testing is ultimately about protecting your people. Identifying and closing these gaps creates a safer environment for employees, customers, and everyone who walks through your doors, and it builds the kind of security awareness that spreads through an organization long after the test is over.
Beyond safeguarding data and physical assets, this testing is ultimately about protecting your people. Identifying and closing these gaps creates a safer environment for employees, customers, and everyone who walks through your doors, and it builds the kind of security awareness that spreads through an organization long after the test is over.
Testing Can Look Different Depending on
What You Want to Know
Physical testing can be run several different ways, often in combination, to fit exactly what you’re trying to learn.
These are some of the most common starting points:
Joint Walkthrough Assessment
Business Hours Assessment
Building Security Assessment
Don't Trust the Replacement Delivery Guy
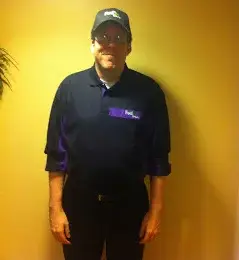
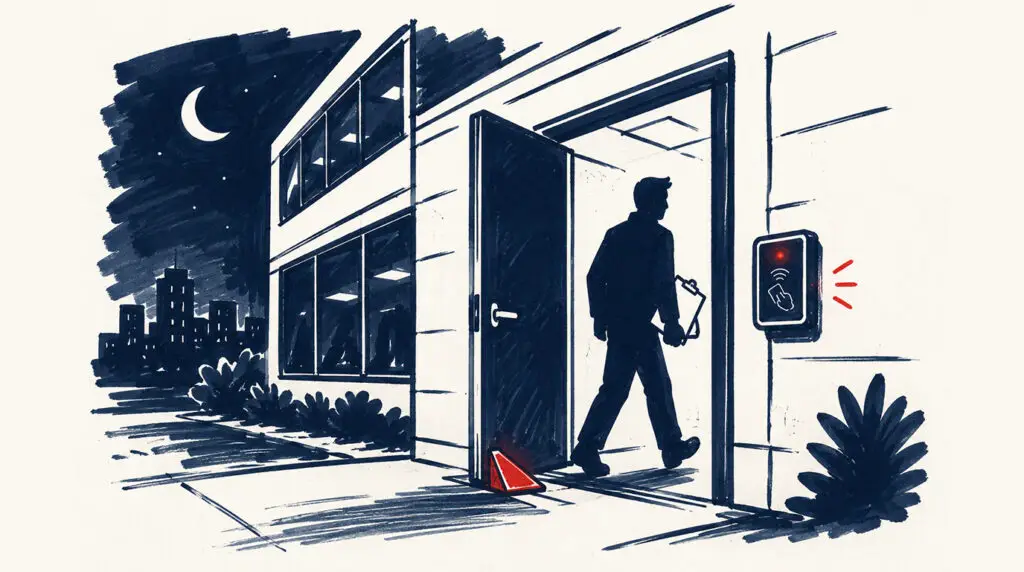
Years ago, our CEO Kevin Tackett bought a delivery uniform on eBay, held a door open for someone on their way out, and walked into a client’s secured office space. He had no badge, there was no reception desk to get past.
Once inside, he found a kiosk workstation with the login credentials written on a sticky note, sat down, and logged into the domain with an account that had domain privileges.
Multiple employees walked past while he was on their network. Every one of them made small talk about the weather. Not one of them asked why a delivery driver was using their computer, or why he had no packages and wasn’t anywhere near the shipping area.
Kevin Tackett, CEO, Secure Ideas
From Consultation to Culture Change
Physical penetration testing follows a similar process to our network and application penetration testing, but has some key differences that are necessary to test a physical location.
This is the typical process for a physical penetration test:
Consultation and Scoping
We discuss your security goals, gather details about your facility's layout and controls, and walk through the methods and any potential risks or disruptions. We do this to ensure everyone has a clear understanding of your needs and goals before anything is signed.
Testing Phase
Our team attempts entry using techniques appropriate to your scope, from counterfeit identification to lock bypass. The consultants document every action and every vulnerability found along the way. We follow the Rules of Engagement (RoE) established beforehand, and carry a Letter of Authorization in case we get caught.
Debrief
Following testing, our testing team and your security team hold a collaborative session to discuss preliminary findings, clarify specific vulnerabilities, and talk through immediate mitigations while everything is still fresh.
Report and Culture Building
The consultants write and provide a detailed report with prioritized recommendations, plus guidance on the training and awareness programs that help to turn a single test into lasting improvement in security culture. These tests are not about weeding out people who “got tricked”, but about building a culture where everyone knows their role in security.

What Happens If Someone Stops Us?
Every physical pentester on-site carries a signed Letter of Authorization (sometimes called a “Get Out of Jail Free” letter) from your organization. If a security guard, an employee, or local law enforcement confronts our team, that letter confirms the engagement is real, approved, and scoped. This helps prevent a legitimate security response from turning into an actual incident. We coordinate in advance on who at your organization knows the test is happening and who doesn’t, based on exactly what you want tested.
Social Engineering
Techniques for social engineering rely on misleading or misdirecting people to pressure them into performing actions or divulging information. Consultants use these techniques to test whether personnel can recognize and resist manipulation attempts commonly used by real-world threat actors to gain initial access, harvest credentials, or extract sensitive information.
For a social engineering engagement, we design each campaign in coordination with the client to establish scope, approved techniques, target populations, and success criteria. These are some of the types of social engineering campaigns that clients request:
Deliverable: Each engagement includes a final report with detailed metrics, examples of successful and unsuccessful attempts, and recommendations to improve security awareness training.
Physical Security Testing
Testing physical security controls include controlled physical intrusion attempts using tailgating, badge cloning, and lock bypass, as well as dumpster diving, and social engineering of on-site personnel. Every engagement operates under clearly defined rules of engagement, including approved facilities, restricted areas, escalation procedures, and a letter of authorization carried by all testers. Testers may perform the following tasks:
Deliverable: Each engagement includes a final report with all access attempts documented with photographs and detailed narratives, identifying gaps in physical controls and personnel awareness.
Pricing: $340/hour | $2,720/day | 1 credit per day | Scoped per engagement.
An evaluation of your security program against the PCI Data Security Standard, covering PCI security assessments, self-assessment support, and advising on scope, applicability, and controls. You get direct access to a Qualified Security Assessor who speaks plainly and knows the standard inside and out.
Led by the “PCI Guy” himself – Jeff Man.
Beyond the Test
New Hires Don't Inherit Your Security Culture Automatically
A single physical pentest tells you how your facility held up on one particular day, with the staff who happened to be working then. Any number of factors could mean that you get different results on another day: Turnover, new office layouts, or a security team that gets comfortable. PETaaS® (Professionally Evil Testing as a Service) lets you deploy prepaid credits across physical testing, social engineering, and other services as your organization changes, with advisory support built in at no additional cost.
A held door doesn’t check anyone’s badge. Keep testing whether your people still would.
Physical
Pentesting
Frequently
Asked
Questions
Have a question that isn’t answered here?
See our full FAQ page.
Is physical penetration testing legal?
Yes, when it’s properly authorized. Every engagement is scoped in advance with your organization’s written approval, and our testers always carry a Letter of Authorization when they’re on-site. Our consultants perform non-destructive bypass techniques unless authorized to do otherwise.
What happens if a guard or employee stops your tester?
This is actually a good outcome. In these instances, our tester presents the Letter of Authorization, and pauses testing until the challenge is resolved. We treat a challenge as a data point about how well your team is paying attention, not a problem to avoid.
Will our security staff know the test is happening in advance?
That depends on what you want to learn. Some engagements involve only a small control group at the top of the organization, while others use a joint walkthrough where staff know from the start. We’ll help you decide during scoping.
Could testing damage our locks or property?
We prioritize non-destructive bypass techniques like shimming over traditional lock picking whenever possible, and we coordinate with you on acceptable methods and any risk of damage before testing begins.
How is this different from a red team engagement?
The difference is in the focus of testing:
- Physical testing focuses specifically on facility access and physical controls.
- A red team engagement is broader and longer, combining physical access with network and application attacks toward a specific objective over weeks or months.
What do we get at the end?
A detailed report documenting each of our access attempts, with photographs and narratives. These findings will identify gaps in physical controls and personnel awareness, and all come with prioritized recommendations you can act on.
Can we see a sample report from a Penetration Test?
Absolutely. Any reputable penetration testing company should provide sample reports upon request. Reports are your primary deliverable and should include an executive summary, testing narrative, detailed findings with risk ratings, replication steps for verification, and actionable remediation recommendations. Not all reports are created equal, so reviewing samples helps ensure the format and content meet your needs. Most companies will accommodate reasonable modifications to reporting formats.
What is Professionally Evil Testing as a Service (PETaaS®)?
Other Pentesting Focuses
Network Penetration Test
Network Pentesting looks at whether an attacker could reach sensitive systems or data through your network, from inside or out. We can test external IP ranges, internal ranges, or a combination, using the same techniques adversaries would try. Our team can design engagements as assumed compromise, controls testing, red team exercises, or network segmentation reviews, depending on what you need to validate.
Trusted for company-driven and regulatory testing alike.
Application Penetration Test
Application Pentesting digs past the obvious and into how your app actually behaves under pressure. Choose a gray box test, a collaborative session with your dev team, SDLC-aligned testing, an authenticated scan, or whatever fits your release cycle. We cover the OWASP Top 10 and beyond, testing internal and external apps against PCI DSS, HIPAA, SOC, and other standards.
We find what the automated scan missed.
API Penetration Test
API Pentesting examines how your interfaces hold up against unauthorized access and abuse, not just whether they return the right response. Our consultants manually test authentication, authorization, and data handling across your endpoints, going beyond what documentation and automated scanners catch. We work to tailor engagements to your architecture, whether you’re testing one API or several that work together.
Manual testing built around how your API is actually used.
Mobile App Penetration Test
Mobile App Pentesting evaluates your app’s code, storage, and communication before it ever reaches your users. We manually assess how the app responds to different inputs, review the code for weaknesses, and attempt access using unauthorized credentials. Testing can run alongside API assessments when your mobile app and backend share risk.
Before it hits the app store, it hits our team.
OT Penetration Test
OT & ICS/SCADA Pentesting searches for potential vulnerabilities to your industrial and automation control environments, without putting production availability at risk. We combine passive and active information gathering across the full stack, from physical access to application layer, tailoring each engagement to your sector.
Testing designed around uptime, not just findings.
IoT & Embedded Device Penetration Test
IoT & Embedded Device Pentesting calls for a different skill set: hardware, firmware, and assembly knowledge layered on top of standard application and API testing. Our consultants have hands-on experience with tons of devices, including door access systems, DVRs and IP cameras, medical devices, sensor nodes, and network appliances. We scope the engagement around the systems, services, and activities specific to your device.
Built for product launches and post-launch confidence alike.
Wireless Penetration Test
Wireless Pentesting takes a close look at your Wi-Fi implementation from three angles: configuration, authenticated access, and an external, unauthenticated perspective. We review your configuration exports for misconfigurations, validate authentication and segmentation controls, and test whether an outsider could capture and crack your pre-shared key. Testing can happen on-site or remotely using our SIAM devices, and these engagements pair nicely with an internal network pentest.
Remote testing options that cut cost and turnaround time.
Recognized authority and trusted guidance built on years of uncovering risks for organizations like yours.
Identifying overlooked vulnerabilities, validating security investments, meeting compliance requirements, and testing whether staff actually follow the policies.
What is Physical Security?
