PROFESSIONALLY EVIL KNOWLEDGE BASE
Practical Pentesting Advice
Written in Plain Language
If you’re looking at getting a pentest done, you have questions: Cost, timelines, scoping, what a report looks like… Many of these questions go unanswered until the sales call, but we’re here to provide some of that information before you pick up the phone. This is where we cover pricing, methodology, and what to expect, in plain language, before you ever talk to us.
Scheduling a penetration test means you are not waiting around for a breach to tell you where security gaps might exist within your environment. However,...
This article describes the main factors we take into account when estimating the cost of a web application penetration test....
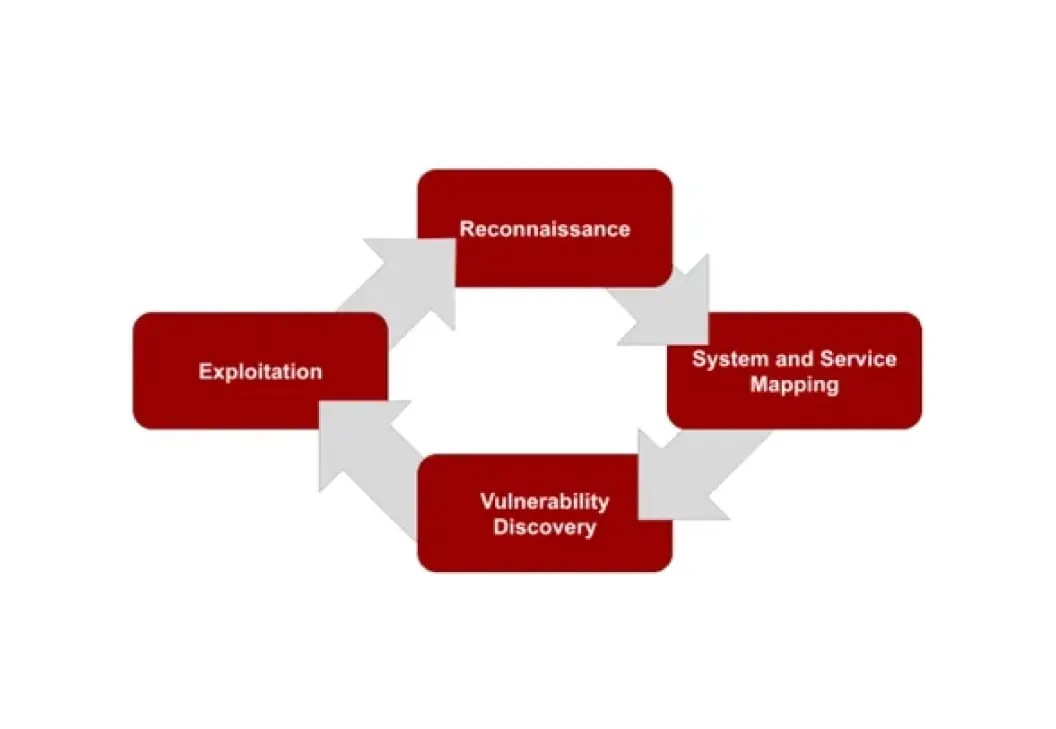
Learn about Secure Ideas' four-step penetration testing methodology: Reconnaissance, System Mapping, Discovery, and Exploitation in a cyclical process....
This article describes the main factors we take into account when estimating the cost of a mobile application penetration test....
This article describes the main factors that we take into consideration while estimating the cost of an internal penetration test....
This article describes the main factors we take into account when estimating the cost of an API penetration test....
Understand the critical differences between vulnerability scans and penetration tests to ensure compliance with security frameworks and accurately assess your risk....
This article describes the main factors that we take into consideration while estimating the cost of an external penetration test....
This article outlines the main factors that impact the effort and cost of the reporting phase of a penetration test engagement....
This article describes what is included in GLBA Compliance Penetration Testing and how it helps educational organizations meet GLBA obligations....
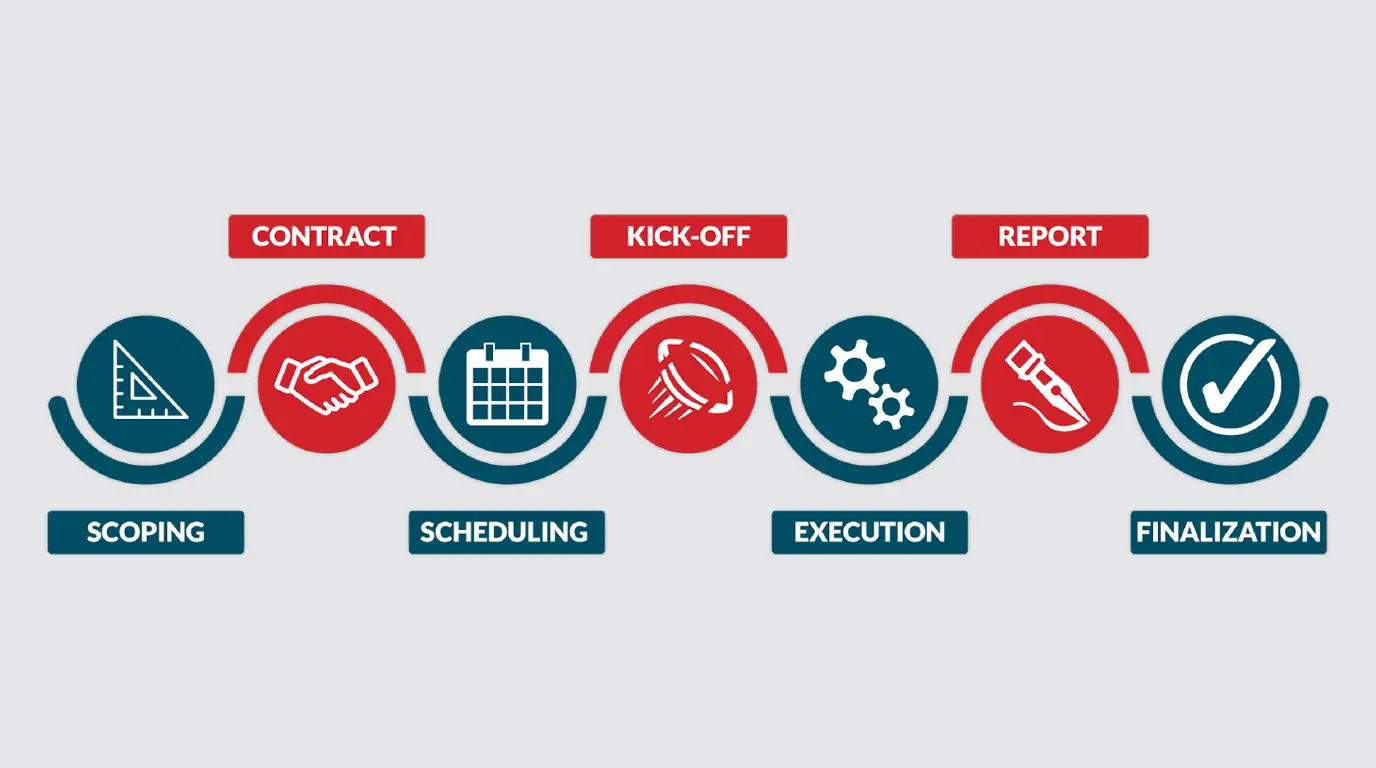
This article describes the main steps in the process for engaging Secure Ideas for penetration testing and consulting services....
Our clients often ask about the specific tools we use during a pen-test and the rules of engagement we adhere to ensure the security and...