
Everything You Need To Know About The Nist Cybersecurity Framework 2.0
This week NIST released the highly anticipated update to the Cybersecurity Framework (CSF). Here’s everything you need to know about v2.0.
Navigating Evolving Regulations: Staying Ahead of Change
Regulatory landscapes across industries are shifting dramatically due to technological advances, geopolitical events, and societal changes.
What are the key requirements of the GLBA Safeguards Rule?
A walkthrough of the details surrounding the GLBA Safeguards Rule and the main components required for your information security program.
Run as Admin: Executive Order on Cybersecurity
On May 12, 2021, President Biden issued an executive order on cybersecurity.
Compliance is not Security
Many folks get confused about the difference between security and compliance. Many, especially those less technically inclined, assume that fulfilling…
Not Just Another Notch in Your Belt: Organizational Challenges of PCI Compliance
Questions surrounding PCI compliance and the challenges organizations face with ensuring proper controls are in place, and all requirements met.
Tips for Penetration Testing a PCI environment
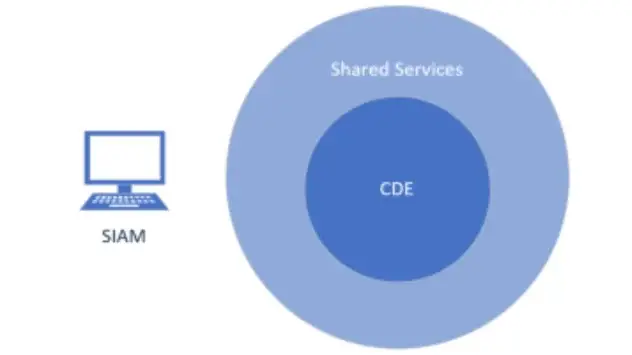
A list of things to help me keep my PCI testing on track, not to mention just as a guideline to start discussions among others doing similar testing.
Practical Pentest Advice from PCI

The PCI Security Standards Council released a Penetration Testing Guidance information supplement in March 2015.
The ABC’s of ASV’s & PCI
Secure Ideas’ prides itself on providing the highest level of service to our customers. We are tirelessly searching for new tools, and methods to use…
Policy Gap Analysis: Filling the Gaps
In the business world there are policies that define how employees should present themselves as well as how company equipment can be used.