
The Report
Being a pen tester is a cool job, we get to break into companies (with permission), steal stuff, and then tell them how we did it.
Are You Ready for Your Pen Test?
It is day three of a five-day penetration test engagement and we still don’t have all the information we need to proceed with the test.
Red Teaming – Not What You May Have Thought
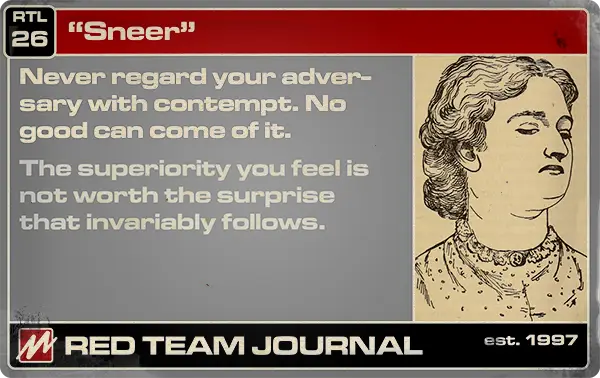
I’ve been doing a lot of reading on some less technical topics and I ran across “Red Team: How to Succeed By Thinking Like the Enemy” by Micah Zenko.
Patching binaries with Backdoor Factory

Downloaded binary files from the Internet or grabbed one off of a network share that is used by your organization to store commonly used software?
What Do You Expect From A PenTest?
There are many reasons that a company has a penetration test performed. Due to regulatory compliance, like HIPAA, or they are just take security seriously
Purple Teaming for Success
You know what blue teams and red teams are. Red is our attack side, or the adversaries, and Blue is the defense side.
SIAM: Custom Testing Machines
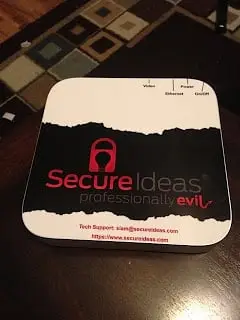
Secure Ideas recently made the decision to create custom machines that we could use for penetration testing engagements.
Industry Issues: New Vulnerabilities and Marketing Problems
As a consultant, I spend a lot of my time working with organizations and staff to help them improve their security.
Preparing for a Consultant
As security consultants, we regularly travel to clients’ sites and experience a wide range of environments and atmospheres.
Admin Consoles, Default Creds, and Sweet Pwnage
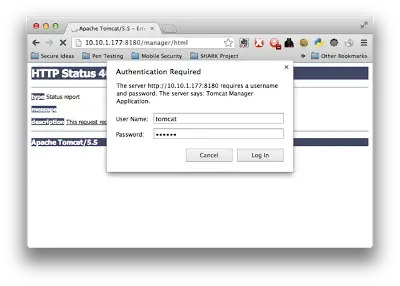
When performing internal network penetration tests, one thing that really gets us excited is finding administrative consoles.