
Twelve Days of XSSmas
This series of daily mini-posts, running from December 12, 2018 to December 24, 2018, is intended to provide cross-site scripting (XSS) related tips.
Three C-Words of Web App Security: Part 2 – CSRF
I identified several types of requests as generally considered safer, and therefore not subject to CORS when being sent across origins.
Silencing Firefox’s Chattiness for Web App Testing
Firefox is one chatty browser! Even if you don’t actually use it for anything, it’s constantly making requests out to the internet for things.
Three C-Words of Web App Security: Part 1 – CORS
For those less versed in web applications and how they’ve evolved, I wrote a sort of prologue to this post back in April 2018.
Going the distance with Burp
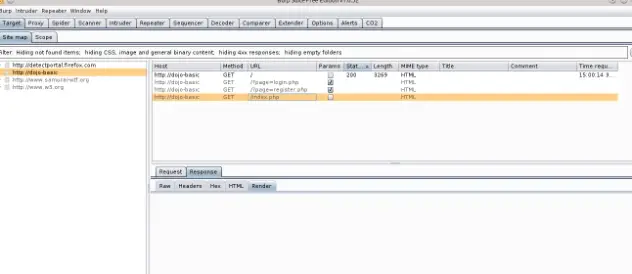
Welcome to the 5th blog on Burp Suite, and Happy 4th of July!
A Brief Evolution of Web Apps

To understand modern mechanisms, it’s helpful to look at what led to their creation.
Burp Suite continuing the Saga
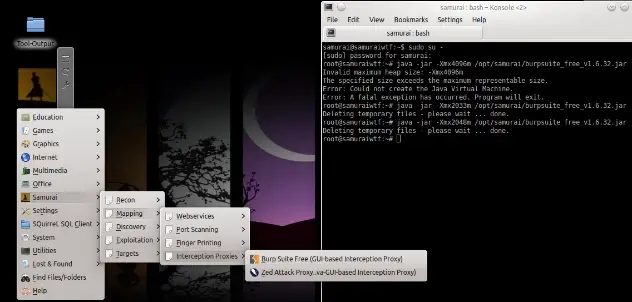
Welcome to the fourth blog introducing and exploring the features of Burp Suite. Please visit Secure Ideas’ previous blogs on using Burp Suite
An Introduction to Javascript for XSS Payloads
I recently got the opportunity to speak at B-Sides Charleston on cross-site scripting (XSS) payload development.
A Brief BeEF Overview
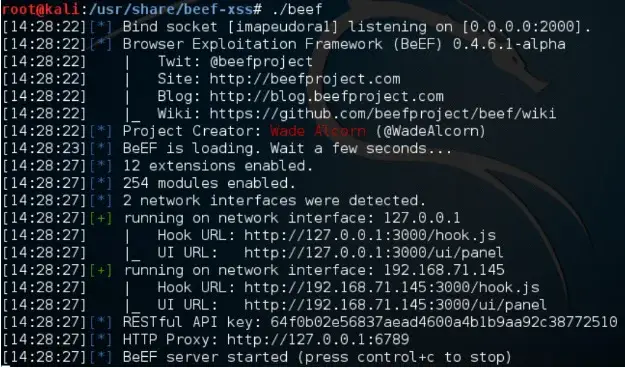
BeEF, the Browser Exploitation Framework, is a testing tool that allows the penetration tester to look past hardened network perimeter and client system..
SQLMap Beginnings: What and How
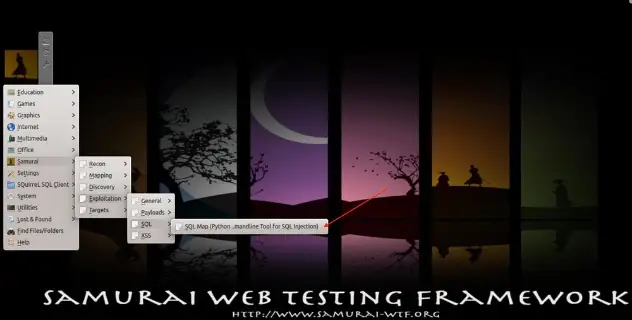
Testing web based applications is not only fun but is often multi-faceted and challenging. Often times a web front end will have places for data input.