PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Password Vampires: Don’t Get Bitten Twice

With Halloween right around the corner, let’s talk about your dark secret from the distant past that could really come back to haunt you: that password you’ve been using since 2015. Don’t lie… You know the one.

...

All Entries

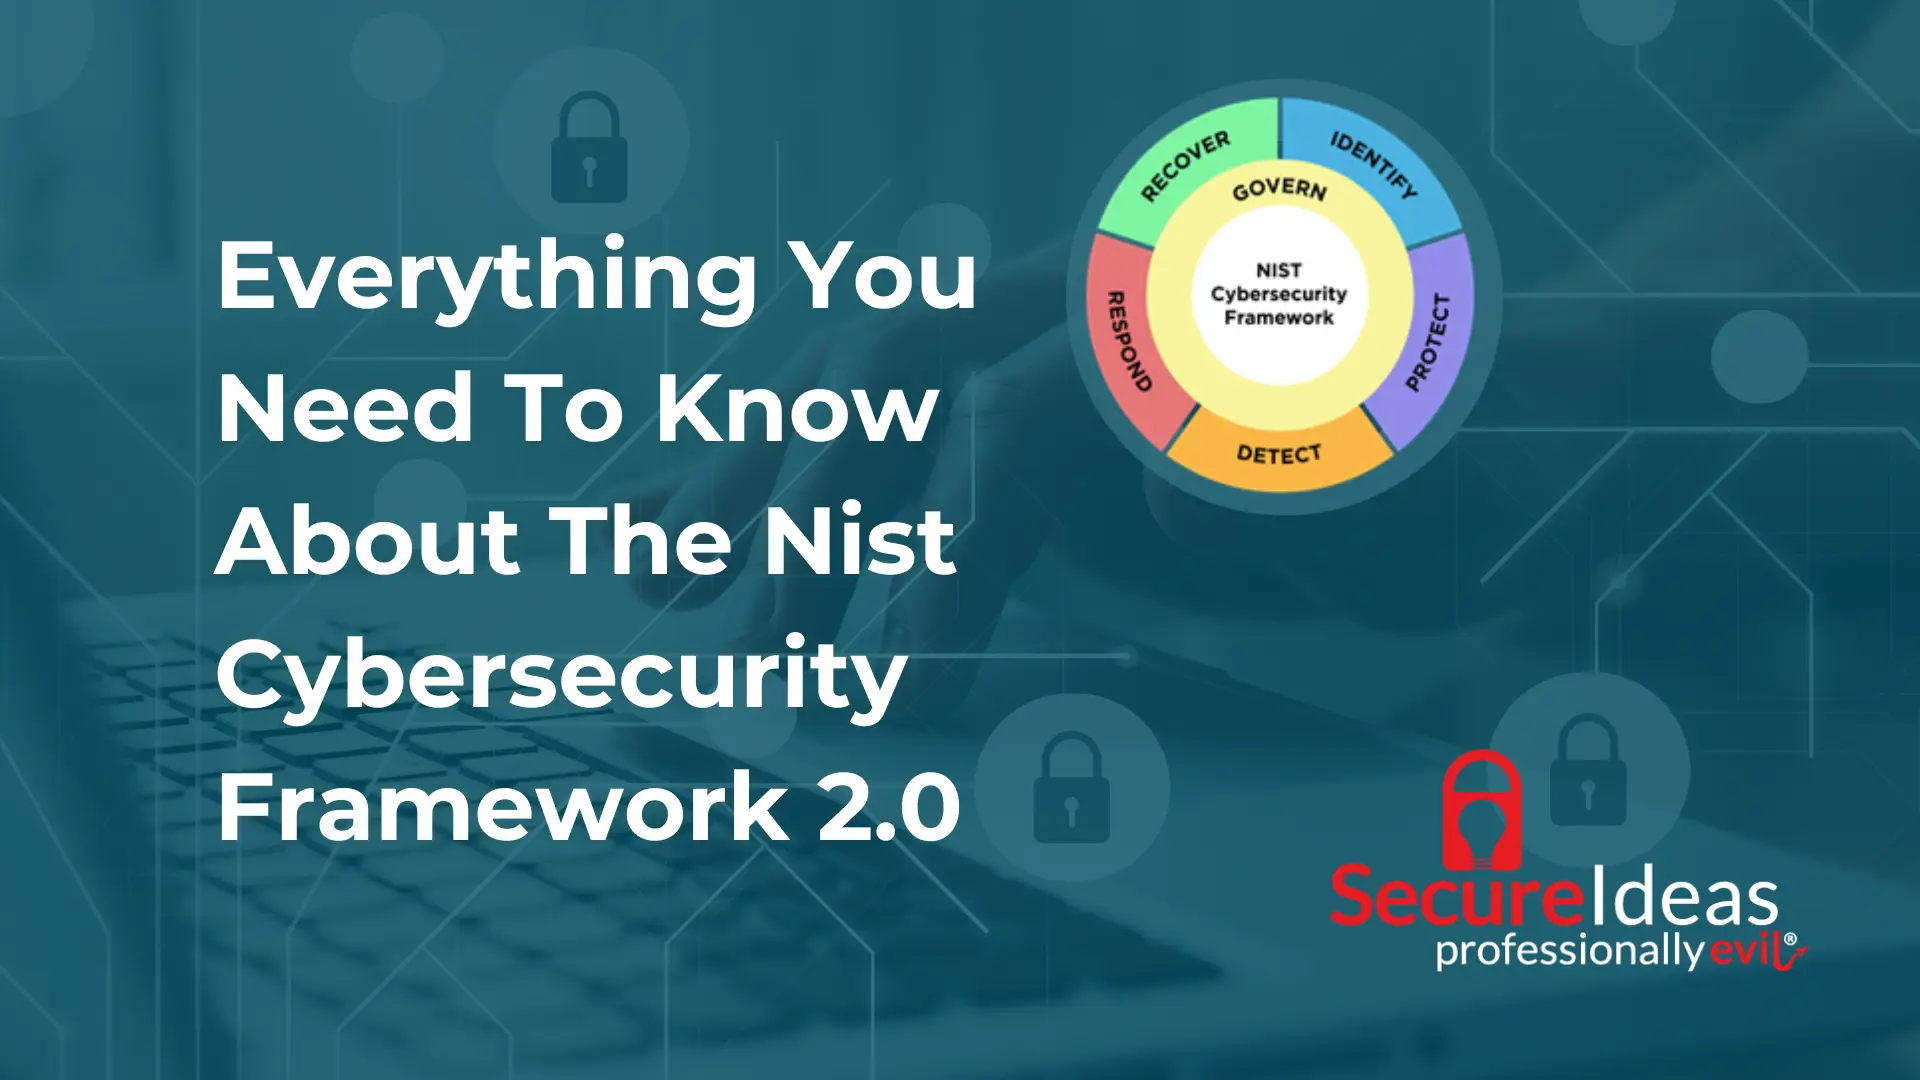
Everything You Need To Know About The Nist Cybersecurity Framework 2.0

Everything You Need To Know About The Nist Cybersecurity Framework 2.0

This week NIST released the highly anticipated update to the Cybersecurity Framework (CSF). Here’s everything you need to know about v2.0....
Does Time Boxed Pentesting Have Value?

Does Time Boxed Pentesting Have Value?

Discover the efficiency of time-boxed penetration testing. Maximize coverage, complement ongoing testing, and address security challenges effectively....
Quick Bites

Quick Bites 9 – Adventuring into the Unknown: The Hacker Subculture

Journey inside the mind of a hacker, maybe learn a thing or two about becoming one yourself....
The reason I stopped using Postman for API Pentests

The reason I stopped using Postman for API Pentests

In May of 2023, Postman announced they were deprecating offline use. This post explores the problem this poses, and Postman alternatives for pentesting....
Mobile Testing Considerations

Mobile Testing Considerations

Discover essential considerations for testing mobile web applications efficiently....
Exploring Sentry Safe Exploit on the Flipper Zero with Logic Analyzer

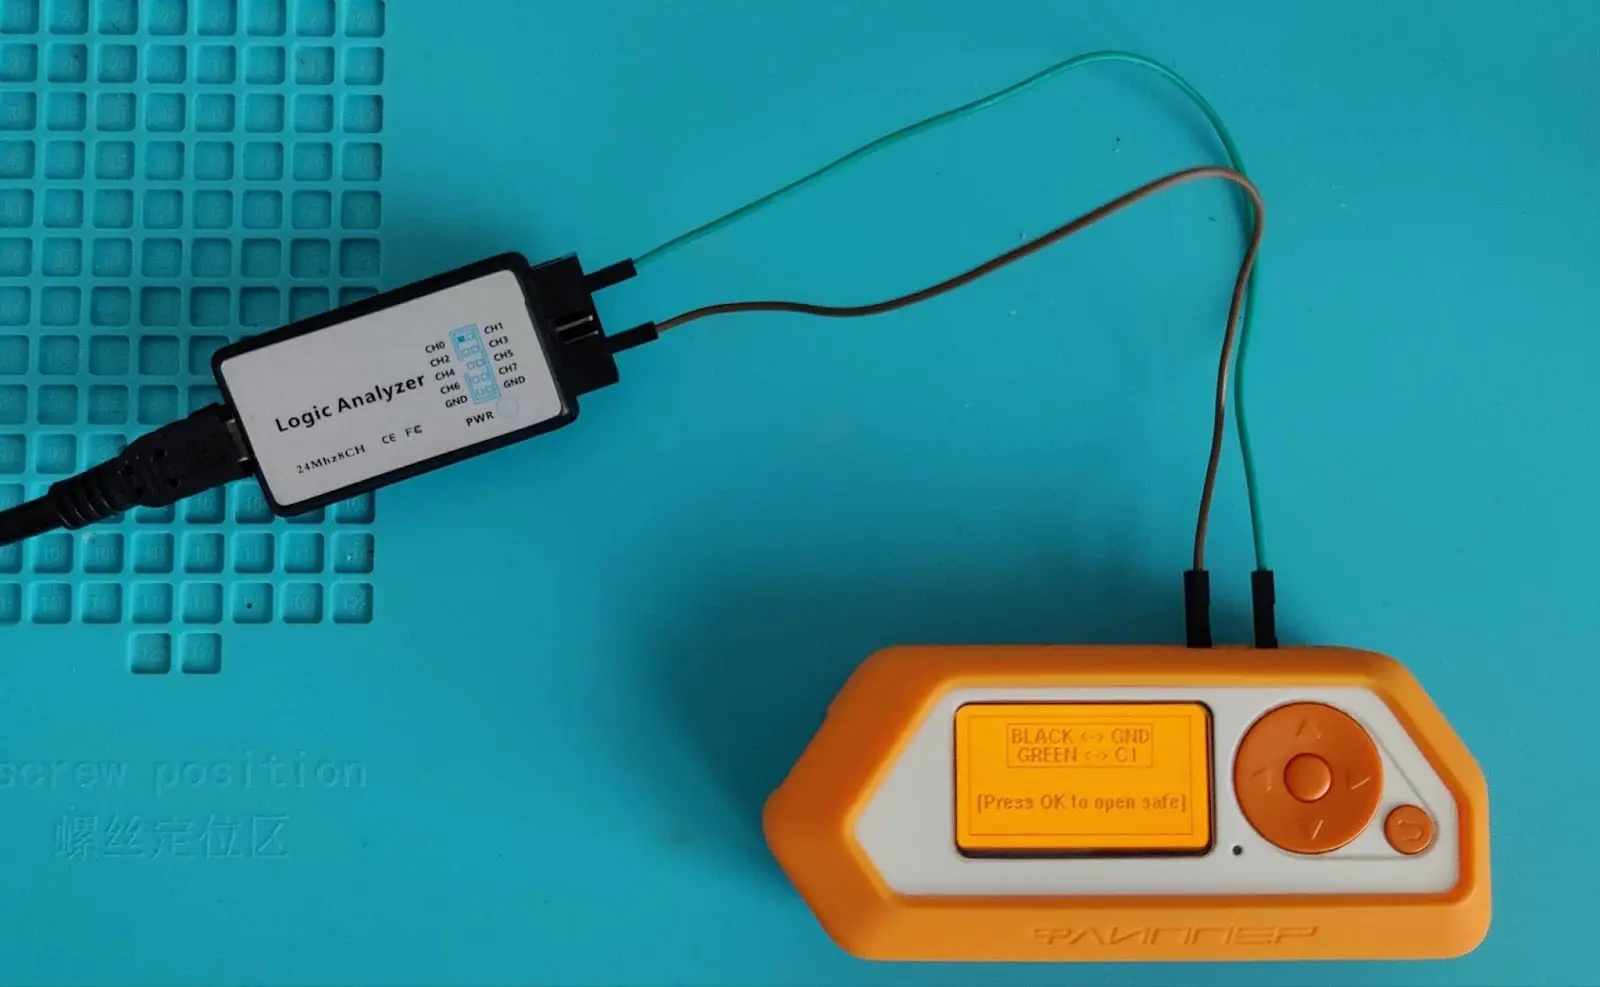
Exploring Sentry Safe Exploit on the Flipper Zero with Logic Analyzer

Learn how to use a logic analyzer to explore the Sentry Safe exploit on the Flipper Zero in this detailed walkthrough....
Webcast: Minor Flaws, Cumulative Risks

Webcast: Minor Flaws, Cumulative Risks

See how a comprehensive approach to cybersecurity can help you anticipate and mitigate risks that small vulnerabilities might pose....
Mission Imfuzzable: How to Fuzz Web Apps you can't Intercept

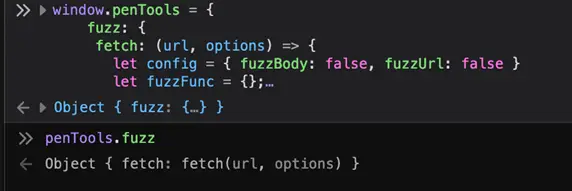
Mission Imfuzzable: How to Fuzz Web Apps you can’t Intercept

This post deals with a real-world scenario of testing a web app that could not be intercepted, and the tooling that came from the solving...
Journey to CISSP

Journey to CISSP

Dive into the Journey of CISSP as our security consultant Kathy Collins talks about her ups and downs earning her CISSP certification....
Webcast: Thrift Store Cracking Server: Popping Hashes Guide

Webcast: Thrift Store Cracking Server: Popping Hashes Guide

Join our webcast on building cost-effective password-cracking servers and optimizing their performance. Gain insights into server builds....
Taming the Enterprise AI Beast Webcast

Taming the Enterprise AI Beast Webcast

As artificial intelligence (AI) continues to become more and more integral to business operations, its security implications cannot be ignored....
12 Hacks of Christmas Day 12: Twelve Drummers Deleting Digital Clutter

12 Hacks of Christmas Day 12: Twelve Drummers Deleting Digital Clutter

Minimizing your digital footprint reduces the risk of exposure to potential cyber threats....

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.