PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Password Vampires: Don’t Get Bitten Twice

With Halloween right around the corner, let’s talk about your dark secret from the distant past that could really come back to haunt you: that password you’ve been using since 2015. Don’t lie… You know the one.

...

All Entries

Paths to Power in Active Directory Part 5: ESC6 Under a False Sigil

Paths to Power in Active Directory Part 5: ESC6 – Under a False Sigil

Explore the risks of privilege escalation in Active Directory through certificate manipulation, highlighting the ESC6 attack path and its implications for security....
Encrypting a Flash Drive in Linux using LUKS

Encrypting a Flash Drive in Linux using LUKS

Learn how to encrypt a flash drive in Linux using LUKS, ensuring data security against loss or theft with step-by-step instructions for beginners....
Beyond the Browser: The Questions That Expanded the Attack Surface

Beyond the Browser: The Questions That Expanded the Attack Surface

Explore how emerging attack vectors like PDF forms in Outlook's preview pane can exploit trusted environments, challenging traditional security assumptions....
What factors impact the cost of a web application penetration test

What factors impact the cost of a web application penetration test?

This article describes the main factors we take into account when estimating the cost of a web application penetration test....
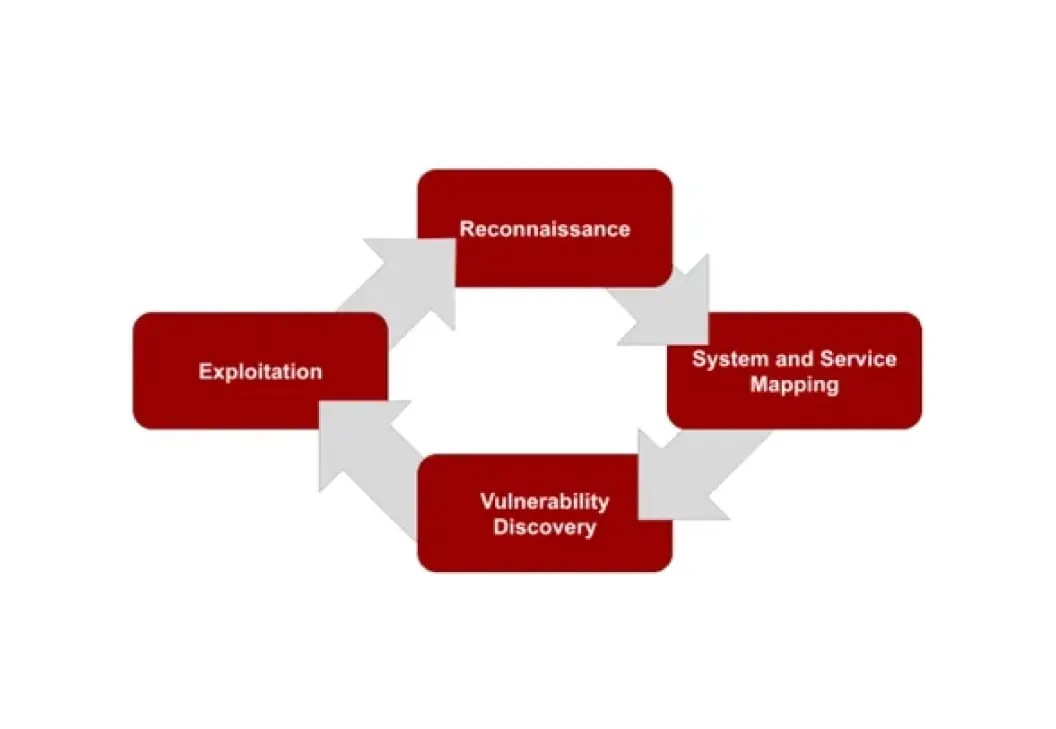
What is your penetration testing methodology?

What is your penetration testing methodology?

Learn about Secure Ideas' four-step penetration testing methodology: Reconnaissance, System Mapping, Discovery, and Exploitation in a cyclical process....
What factors impact the cost of a mobile application penetration test

What factors impact the cost of a mobile application penetration test?

This article describes the main factors we take into account when estimating the cost of a mobile application penetration test....
What factors impact the cost of an internal penetration test

What factors impact the cost of an internal penetration test?

This article describes the main factors that we take into consideration while estimating the cost of an internal penetration test....
What factors impact the cost of an API or microservice penetration test

What factors impact the cost of an API or microservice penetration test?

This article describes the main factors we take into account when estimating the cost of an API penetration test....
I Built the Droid I Was Looking For (AI Pit Droid pt. 1)

I Built the Droid I Was Looking For (AI Pit Droid pt. 1)

A cybersecurity professional builds an AI-powered Star Wars Pit Droid using an NVIDIA Jetson Orin Nano. The story behind the build, the tech, and why...
GLBA Breach Notifications: Is Your Incident Response Program Built for It?

GLBA Breach Notifications: Is Your Incident Response Program Built for It?

Ensure your incident response program meets GLBA breach notification requirements. Learn key insights on compliance and effective response strategies....
PCI DSS 4.0.1 Proving Security: A Penetration Testing Series

PCI-DSS 4.0.1 – Proving Security: A Penetration Testing Series

Annual pen tests check the box, but there's no magic in a snapshot. Explore how PCI-DSS 4.0.1 reframes penetration testing as continuous validation, not a...
Rolling for Resilience Part 5 Side Quests: Not Every Member of the Party Swings a Sword!

Rolling for Resilience Part 5 – Side Quests: Not Every Member of the Party Swings a Sword!

Explore the importance of role-based paths in cybersecurity incident response training, enhancing engagement and realism in tabletop exercises....

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy.