PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Password Vampires: Don’t Get Bitten Twice

With Halloween right around the corner, let’s talk about your dark secret from the distant past that could really come back to haunt you: that password you’ve been using since 2015. Don’t lie… You know the one.

...

All Entries

Step Into the Shadows: The Haunting of the Dark Web

Step Into the Shadows: The Haunting of the Dark Web

Explore the dark web's impact on cybersecurity and learn essential navigation skills in our Halloween webcast with our experts on October 24th....
Automating UART Command Injection with the Flipper Zero and JavaScript

Automating UART Command Injection with the Flipper Zero and JavaScript

Explore the new JavaScript capabilities of Flipper Zero that allows users to create and run custom scripts from the SD card....
A Miopia dos CISO

A Miopia dos CISO

Profissionais de segurança, como CISOs, enfrentam desafios na gestão de riscos sem parceiros externos realizando pentests eficazes....
What’s new in the OWASP Proactive Controls for 2024

O que há de novo nos Controles Pró-Ativos da OWASP para 2024?

Este artigo discute os controles pró-ativos da OWASP Top 10 e as principais preocupações de segurança para desenvolvedores....
What’s new in the OWASP Proactive Controls for 2024

What’s new in the OWASP Proactive Controls for 2024

"Exploring OWASP Top 10 controls and app security for developers...
Many Hands Approach To AppSec

Many Hands Approach To AppSec

Discussion on practical strategies for rolling out an effective application security program and balancing security with development efficiency....
The CISO's Myopia

The CISO’s Myopia

Information security professionals struggle to manage all the aspects needed to create effective policies and processes without external partners...
Kubernetes Pentesting: The Hacker’s Harvest

Kubernetes Pentesting: The Hacker’s Harvest

Learn from experts and gain valuable knowledge to fortify your Kubernetes environment in this webcast...
The Evolution of Penetration Testing

The Evolution of Penetration Testing

Penetration testing is much more than a checkbox exercise. Organizations recognize this and are turning to PETaaS, allowing them to reap the benefits....
From Code to Cloud: Strengthening IaC Security with SAST

From Code to Cloud: Strengthening IaC Security with SAST

Scale and integrate security best practices into IaC reviews for DevOps/DevSecOps. Optimize tools and cloud provider practices for enhanced security....
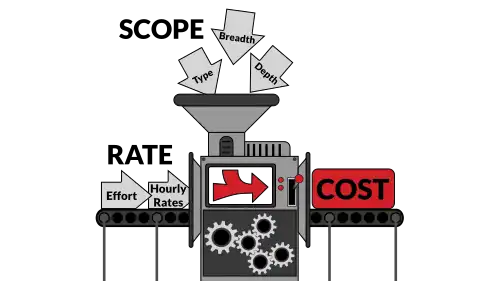
How much does a Penetration Test Cost?

How much does a Penetration Test Cost?

This article describes what the cost of a penetration test from Secure Ideas is, as well as ways to affect the final bill....
Straight Facts: Testing as a Service Dispatches the Goods

Straight Facts: Testing as a Service Dispatches the Goods

Most InfoSec professionals see rapid tech advances changing security approaches, prompting the need for solutions beyond the status quo....

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy.