
The Secret Handshake – Covertly Redirecting Mobile Traffic to a Different Backend
Learn how to covertly redirect mobile app traffic to different backends during penetration tests, overcoming common challenges with Burp Suite and mitmproxy.
Paths to Power in Active Directory Part 1: How AD CS Misconfigurations Become the Keys to the Kingdom
From regular domain user to Domain Admin in minutes. Discover how AD CS misconfigurations create one of Active Directory’s most abusable attack paths.
Annual Pentests Aren’t Cutting It Anymore: Why Continuous Testing Beats Scrambling at Renewal Time
From annual fire drill to continuous security: Why PCI DSS, HIPAA, and cyber insurance requirements are pushing organizations toward ongoing testing.
Quantum Leaping Through Data: Preparing for the Quantum Encryption Transition
Quantum computers will break current encryption within 10 years, but adversaries are harvesting your data today. Your migration window is narrower than you think.
Your Risk Framework Is Broken: The Al Reality Check Every CISO Needs
AI eliminated the attack complexity barriers your risk frameworks rely on. CVSS, NIST, and OWASP assumptions are obsolete. Here’s the audit you need today.
Best Practices and Risks Considerations in Automation like LCNC and RPA
Best practices and risk considerations in using Low-Code/No-Code (LCNC) and Robotic Process Automation (RPA) for digital transformation and automation.
Everything You Need To Know About The Nist Cybersecurity Framework 2.0
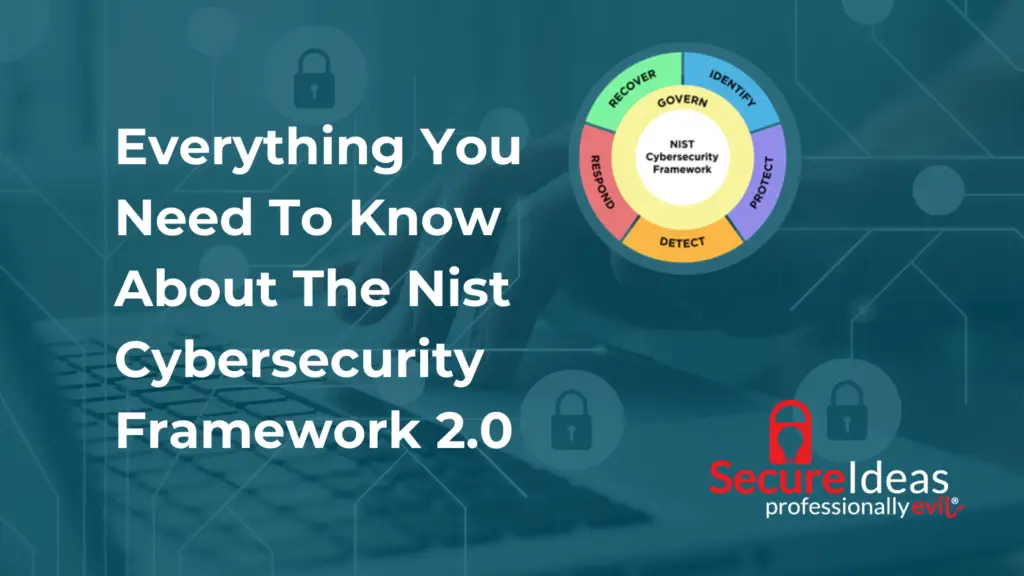
This week NIST released the highly anticipated update to the Cybersecurity Framework (CSF). Here’s everything you need to know about v2.0.
Essential Security Requirements for Application Development
Explore common security requirements for customer-facing applications.
Beyond Hacking: Expanding Your Security Arsenal
Maybe you are coming from an organization that recently fell under broadened regulations (like higher education institutions and GLBA).
A Step-by-Step Guide to Penetration Testing for Beginners
Describes penetration testing, step by step, for those who are new to pentests.