
The Secret Handshake – Covertly Redirecting Mobile Traffic to a Different Backend
Learn how to covertly redirect mobile app traffic to different backends during penetration tests, overcoming common challenges with Burp Suite and mitmproxy.
Building a Custom Burp Suite Collaborator Everywhere BApp

Learn how to customize Burp Suite’s Collaborator Everywhere BApp using Docker and Gradle for better compatibility with your client’s web applications.
Twelve Days of ZAPmas – Day 11 – ZAP impressions from a Burp user
Day 11 of the series makes a comparison of ZAP versus Burp from the perspective of a long-time Burp user who is relatively new to ZAP.
Hunting Secrets
A rundown of the Secrets Hunter capability within Paramalyzer, used to quickly find instances of sensitive information leakage in web applications.
Announcing Burp Co2!

Over the past couple of months I have been using my Java skills to build a collection of Burp extensions that have been dubbed “Co2”.
Proxying HTTPS Traffic with Burp Suite
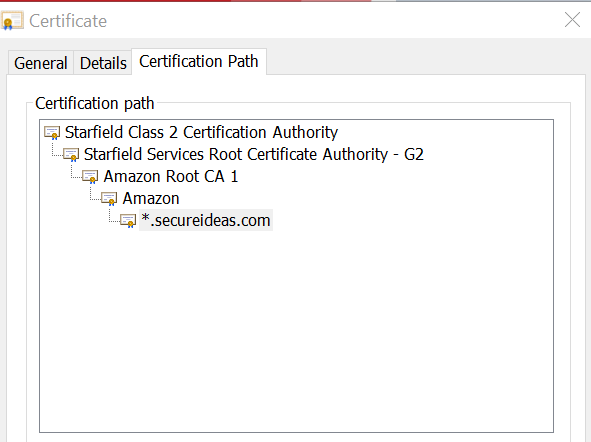
Because every new installation of Burp generates a different CA, this doesn’t create a risk of somebody else intercepting your traffic surreptitiously.
Going the distance with Burp
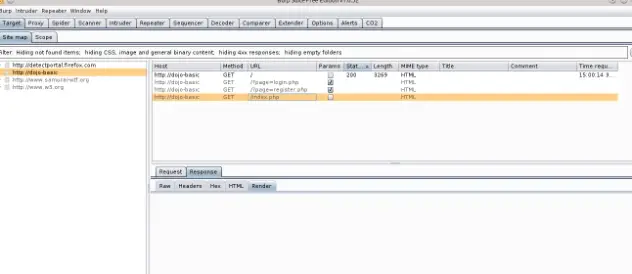
Welcome to the 5th blog on Burp Suite, and Happy 4th of July!
Burp Suite continuing the Saga
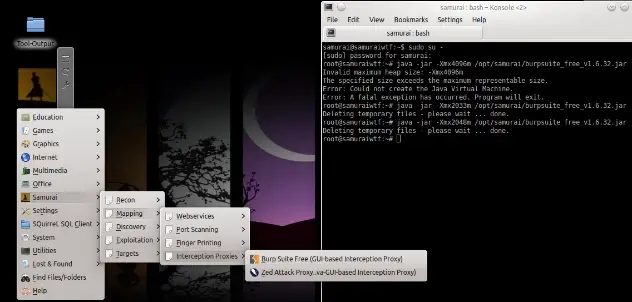
Welcome to the fourth blog introducing and exploring the features of Burp Suite. Please visit Secure Ideas’ previous blogs on using Burp Suite
Introducing Burp Correlator!
This new Burp extension is designed to help with efficiency when you are testing a complex application full of parameters or a series of applications.
Tip: Running BurpSuite on a Mac
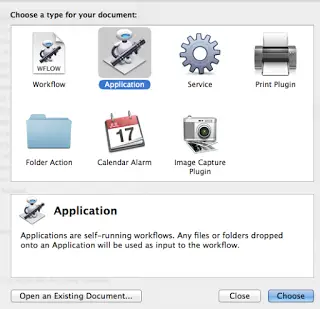
Quick tip to save some time when spinning up Burp Suite on a Mac. Use Burp Suite frequently enough that having an icon on my task bar is warranted.