
What is the Secure Ideas engagement process?
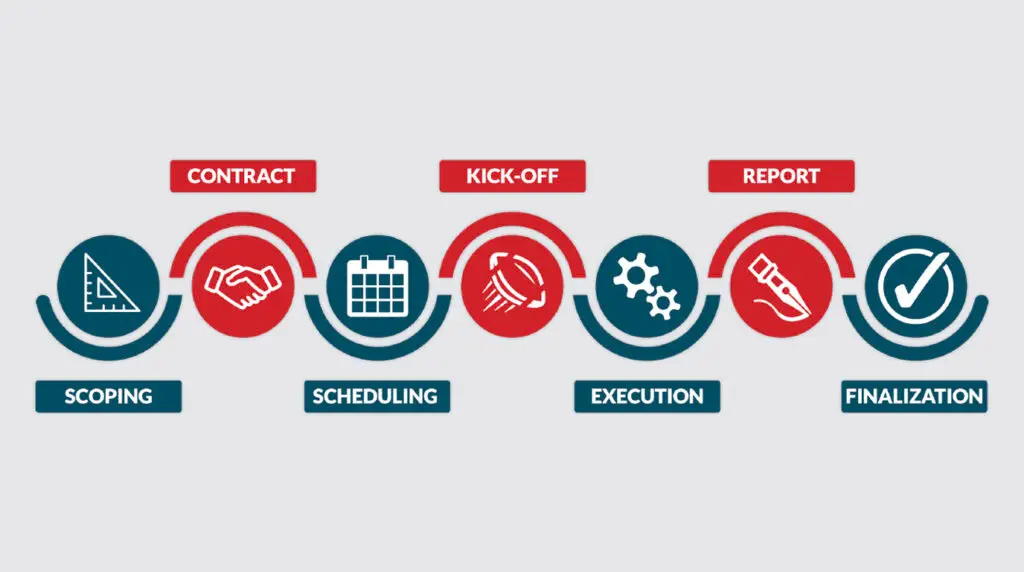
This article describes the main steps in the process for engaging Secure Ideas for penetration testing and consulting services.
CyberScream – Hacking Like a Ghost(face)
In this webcast, we’re discussing breaches and horror movies. Grab your hunting knife and get ready to hack (and slash) through some noteworthy news.
How is Embedded/IoT Scoping Different from a Normal Pentest?

An article outlining some things you may want to think about when they are considering a test of an embedded or IoT device due to their ecosystem nature.
(Not So) Quick Bites – Episode 3 – Writing About Writer’s Block
On this (Not So) Quick Bites, we’re talking about writer’s block, and how to get over it. Here’s five tips and tricks that I use to get to writing.
Project Responsibilities
This page details the responsibilities for a project
What Sets Secure Ideas Apart From Other Security Consulting Firms?
This page outlines Secure Ideas’ experience and expertise in the field of information security
10 Tips for Engaging a Security Services Vendor
With huge growth comes an avalanche of security companies promising to fix all of your cyber worries.
Professionally Evil: Self Inflicted Injury at Vendor’s Request
It’s an unfortunate and still too common a vulnerability to find administrative interfaces exposed and configured with default passwords.
Preparing for a Consultant
As security consultants, we regularly travel to clients’ sites and experience a wide range of environments and atmospheres.