
Journey to CISSP
Dive into the Journey of CISSP as our security consultant Kathy Collins talks about her ups and downs earning her CISSP certification.
Quick Bites 7 – Dr. TamperMonkey (Or: How I Learned to Stop Worrying and Love JavaScript)
In this episode of Quick Bites, you will learn some tips on writing your own browser-based userscripts.
Application Security 101
Application security is a big job, for sure. And it’s not just the job of the developers or the SOC. There is an incredible amount of surface to cover.
PowerShell Tips: How do I Mount a VHD or Lock a BitLocker Drive?
A blog post about using Windows PowerShell to quickly mount or lock a VHD, or BitLocker encrypted drive.
Linux X86 Assembly – How to Build a Hello World Program in GAS
How to build a 32-bit x86 Hello World program in NASM using the GAS toolchain.
Linux X86 Assembly – How to Build a Hello World Program in NASM
We as humans use mnemonics to make building these instructions easier than remembering a bunch of binary codes.
Getting Started API Penetration Testing with Insomnia
In our blog series on Better API Penetration Testing with Postman we discussed using Postman as the client for testing RESTful service APIs.
Are You Ready for Your Pen Test?
It is day three of a five-day penetration test engagement and we still don’t have all the information we need to proceed with the test.
Introduction to Burp Suite Webcast

The below video is an introduction to Burp Suite. This is the first of our videos that will teach people how to use Burp Suite and other tools the same…
Getting Started with BeEF: The Browser Exploitation Framework
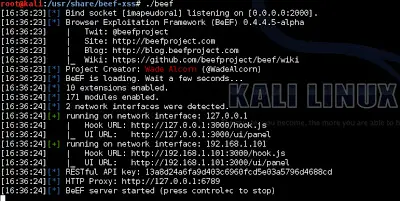
This post is the first in a series on Getting Started with information security tools.