
Twelve Days of ZAPmas – Day 4 – Fuzzing for Injection
The fourth day of the series introduces using ZAP’s Fuzzer tool to fuzz for injection flaws in the client (XSS) and server.
Twelve Days of ZAPmas – Day 3 – CYA (Cover Your Auth)
The third entry in the Twelve Days of ZAPmas series deals with using Zed Attack Proxy’s request tampering to check if your authorization controls work.
Twelve Days of ZAPmas – Day 2 – The Edge of Tomorrow
This second post in the 12 day series uses OWASP Zed Attack Proxy to modify and replay traffic we captured on day 1.
Twelve Days of ZAPmas – Day 1 – Setting Up ZAP
This post kicks off the 12 day series by setting up OWASP Zed Attack Proxy and walks through the manual steps to setup Chrome or Firefox to proxy through.
Quick Bites – Finding Open Windows File Shares
How to find open Windows network file shares and secure them with publicly available tools. Lock down your network shares!
PowerShell Tips: How do I Mount a VHD or Lock a BitLocker Drive?
A blog post about using Windows PowerShell to quickly mount or lock a VHD, or BitLocker encrypted drive.
Converting NMAP XML Files to HTML with xsltproc
NMAP is a wonderful network scanner and its ability to log scan data to files, specifically XML, helps quite a bit.
Tip: Running BurpSuite on a Mac
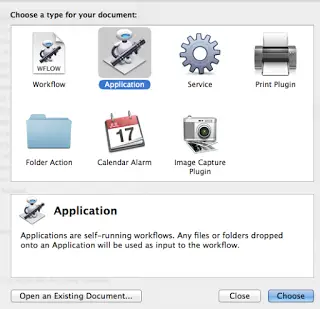
Quick tip to save some time when spinning up Burp Suite on a Mac. Use Burp Suite frequently enough that having an icon on my task bar is warranted.
Creating SSL Certificate Requests Using Certreq.exe and Enable LDAPS
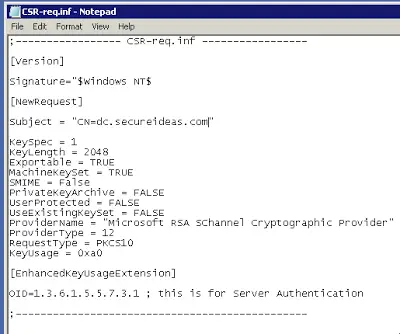
This post picks up on my last about creating and authorizing an internal certificate authority.
SSL Certificates: Setting Up and Authorizing the Internal Certificate Authority
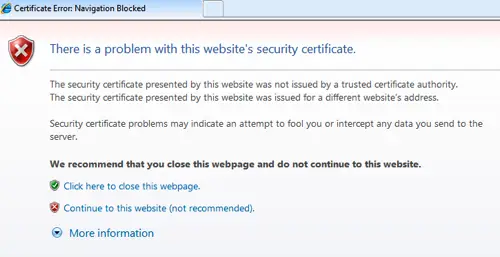
In this post, I wanted to give something directly to the Blue Teams out there.