
Supply Chain Security: Trust Is the New Attack Surface
Securing the software supply chain requires continuous validation of trust, not just reliance on outdated third-party risk practices.
A Miopia dos CISO
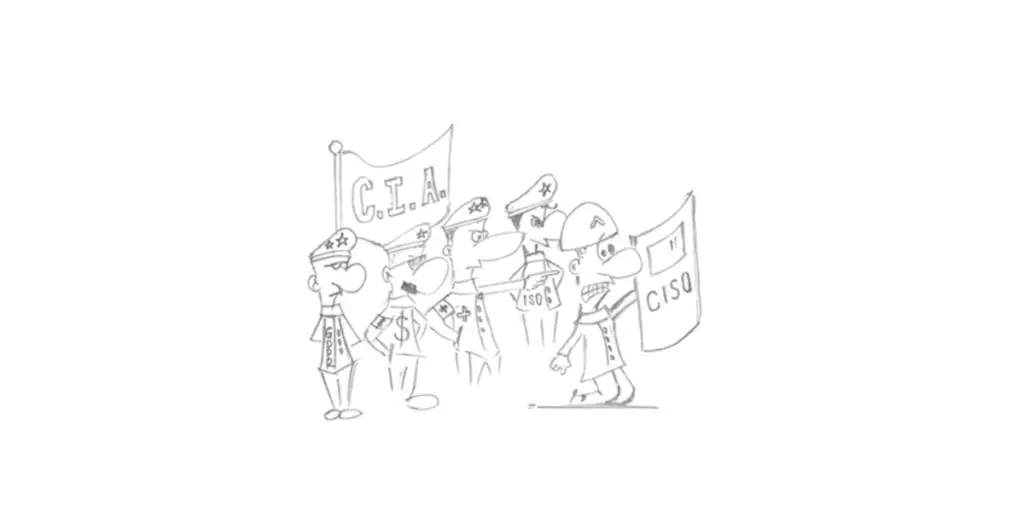
Profissionais de segurança, como CISOs, enfrentam desafios na gestão de riscos sem parceiros externos realizando pentests eficazes.
The CISO’s Myopia
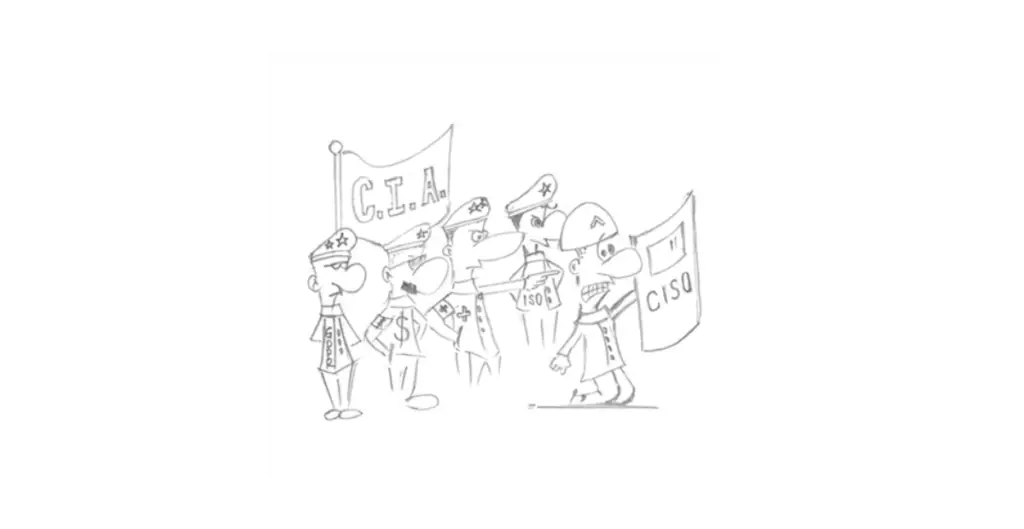
Information security professionals struggle to manage all the aspects needed to create effective policies and processes without external partners
Straight Facts: Testing as a Service Dispatches the Goods
Most InfoSec professionals see rapid tech advances changing security approaches, prompting the need for solutions beyond the status quo.
Prompt Injection
Discover AI prompt injection with Cory Sabol: understand this AI threat, its impact, real examples, and defenses.
Does Time Boxed Pentesting Have Value?
Discover the efficiency of time-boxed penetration testing. Maximize coverage, complement ongoing testing, and address security challenges effectively.
Using PETaaS to Lower Your Cyber Insurance Costs
Wondering how you can decrease the cost of your cyber insurance? Secure Ideas’ PETaaS is a great way to simultaneously cut costs and increase security.
Navigating Evolving Regulations: Staying Ahead of Change
Regulatory landscapes across industries are shifting dramatically due to technological advances, geopolitical events, and societal changes.
What happened to CVE-2022-23529? And what can we learn from it?
This post digs into how the node_jsonwebtoken vulnerability, CVE-2022-23529, went from being widely heralded as a critical issue to being a non-issue.
What are the key requirements of the GLBA Safeguards Rule?
A walkthrough of the details surrounding the GLBA Safeguards Rule and the main components required for your information security program.