
Bypassing Browser PDF Security: Using Embedded JavaScript Forms for Social Engineering
From PDFs to social engineering, I explore how trusted apps and browsers can be exploited in penetration testing to reveal hidden risks.
Being Safe and Secure with Cross-Origin Messaging
Explore onMessage and postMessage in browsers: Learn cross-origin JavaScript interactions, security issues, and flaw prevention.
Mission Imfuzzable: How to Fuzz Web Apps you can’t Intercept
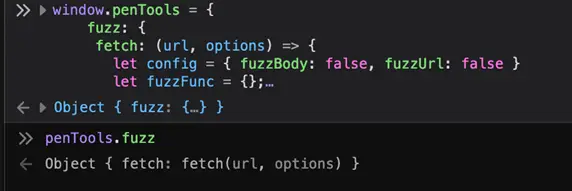
This post deals with a real-world scenario of testing a web app that could not be intercepted, and the tooling that came from the solving that.
Quick Bites 7 – Dr. TamperMonkey (Or: How I Learned to Stop Worrying and Love JavaScript)
In this episode of Quick Bites, you will learn some tips on writing your own browser-based userscripts.