
What is your penetration testing methodology?
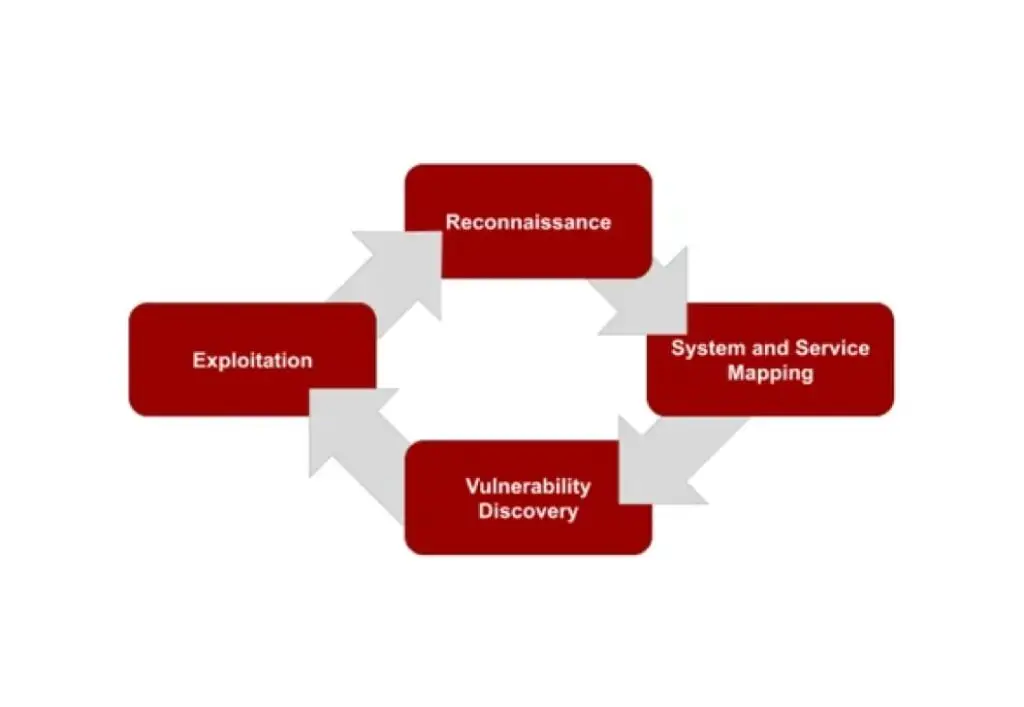
Learn about Secure Ideas’ four-step penetration testing methodology: Reconnaissance, System Mapping, Discovery, and Exploitation in a cyclical process.
What are the Tools and Rules of Engagement at Secure Ideas for Web Application Penetration Tests?
Our clients often ask about the specific tools we use during a pen-test and the rules of engagement we adhere to ensure the security and integrity of their applications. This article aims to address these concerns, providing an in-depth understanding
Finding Your Spidey Sense
As you begin your web app pentesting adventure, it’s essential to understand the treacherous landscape you’re about to explore.
Understanding Server-Side Template Injection (SSTI)
Discover the risks of Server-Side Template Injection (SSTI) vulnerabilities, learn how to detect and prevent them, and safeguard your web applications.
(Not So) Quick Bites – Episode 3 – Writing About Writer’s Block
On this (Not So) Quick Bites, we’re talking about writer’s block, and how to get over it. Here’s five tips and tricks that I use to get to writing.
Secure Ideas’ Penetration Testing Methodology
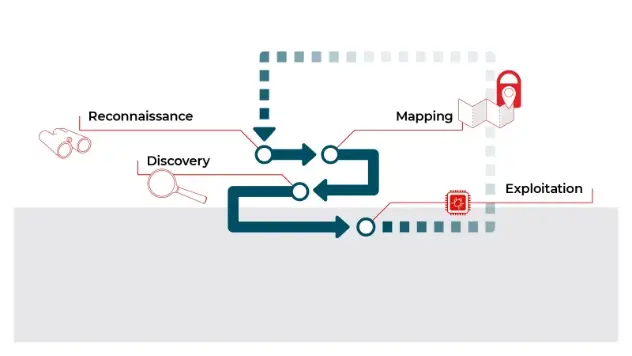
This page provides an in depth explanation of our testing methodology as well as a link to download a copy for your reference
Project Responsibilities
This page details the responsibilities for a project
Quick Bites Episode 2 – HTTP Security Headers and Why You NEED Them
Secure Ideas’ Quick Bites Ep 2 – HTTP security headers are important for webapp security. Here are some that will help lockdown your site a little better.
Quick Bites – Finding Open Windows File Shares
How to find open Windows network file shares and secure them with publicly available tools. Lock down your network shares!
Fuzz Testing
A brand new piece of software, a program, a network, or an operating system, you will want to test it for any bugs, coding errors or other potential issues