
Adventures in LDAP Injection: Exploiting and Fixing

Every pen tester looks forward to that next encounter that includes one of those uncommon vulnerabilities.
Logging Like a Lumber Jack
Turn on any news outlet or visit any news site and you will most likely see an announcement of yet another data breach.
Intercepting DNS
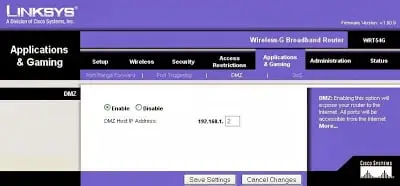
Recently during a penetration test, I discovered a Linksys WRT54G wireless router that had been installed on a customer’s network.
Defending Against Pass-the-Hash (PtH) Attacks
Pass-the-Hash (PtH) attacks have become probably the most common form of credential attacks used in the hacking community.
SSL Certificates: Setting Up and Authorizing the Internal Certificate Authority
In this post, I wanted to give something directly to the Blue Teams out there.
Using a Throwing Star to Capture Packets
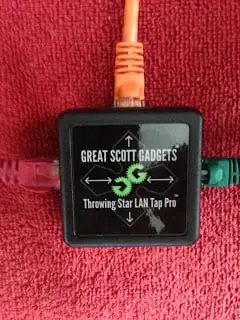
Mobile applications are a hot commodity these days. It seems like everyone and their brother/sister is writing them.
Professionally Evil: This is NOT the Wireless Access Point You are Looking For
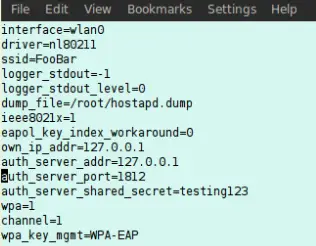
I was recently conducting a wireless penetration test and was somewhat disappointed to find that they had a pretty well configured set of wireless networks
Mining in a corporate environment
We have a virus attack will stop any security professional in their tracks. Even with strict security policies and procedures around patch and anti-virus.