
PCI-DSS 4.0.1 – Proving Security: A Penetration Testing Series
Annual pen tests check the box, but there’s no magic in a snapshot. Explore how PCI-DSS 4.0.1 reframes penetration testing as continuous validation, not a calendar event.
Countdown to Full Compliance: PCI-DSS 4.0.1
Get ready for the PCI DSS v4.0.1 compliance deadline by addressing key requirements like multi-factor authentication, malware scanning, and automated audit log reviews.
What does PCI require for Developer Training?
Understand what the PCI DSS requires for annual developer training.
Essential Security Requirements for Application Development
Explore common security requirements for customer-facing applications.
What is Required for a PCI Penetration Test?
What’s required for a penetration test that complies with PCI DSS 4.0? Learn the details necessary to meet compliance with the new standard.
Not Just Another Notch in Your Belt: Organizational Challenges of PCI Compliance
Questions surrounding PCI compliance and the challenges organizations face with ensuring proper controls are in place, and all requirements met.
Tips for Penetration Testing a PCI environment
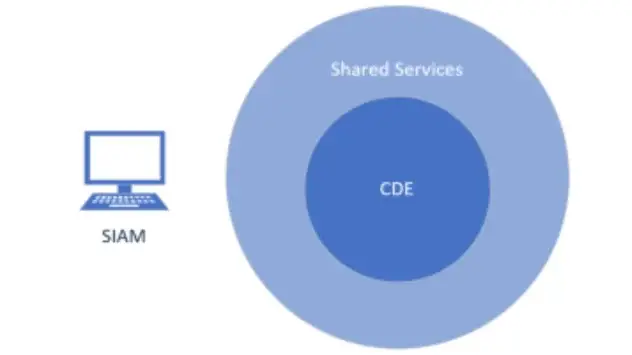
A list of things to help me keep my PCI testing on track, not to mention just as a guideline to start discussions among others doing similar testing.
Practical Pentest Advice from PCI

The PCI Security Standards Council released a Penetration Testing Guidance information supplement in March 2015.
The ABC’s of ASV’s & PCI
Secure Ideas’ prides itself on providing the highest level of service to our customers. We are tirelessly searching for new tools, and methods to use…
Why Target’s Breach Included PIN Data
Last Friday Target issued an update acknowledging that encrypted PIN data were included in the data stolen in their recent breach.