
Twelve Days of ZAPmas – Day 2 – The Edge of Tomorrow
This second post in the 12 day series uses OWASP Zed Attack Proxy to modify and replay traffic we captured on day 1.
What Tasks are Performed During a Hardware Security Assessment?
The knowledge base article covers what you can expect when requesting a security assessment of an IoT or embedded device.
How is Embedded/IoT Scoping Different from a Normal Pentest?

An article outlining some things you may want to think about when they are considering a test of an embedded or IoT device due to their ecosystem nature.
What are the key requirements of the GLBA Safeguards Rule?
A walkthrough of the details surrounding the GLBA Safeguards Rule and the main components required for your information security program.
Penetration Testing Compliance under GLBA in 2024 – What You Need to Know
This article explains regulatory changes under GLBA in 2024 and how to maintain compliance with penetration testing.
Application Security 202: Vulnerabilities Accepted
Studying how to accept vulnerabilities and secure applications
How Soon Can We Schedule a Test?
This article explains when a test can be scheduled and tips for avoiding project delays
How to allow multiple RDP sessions
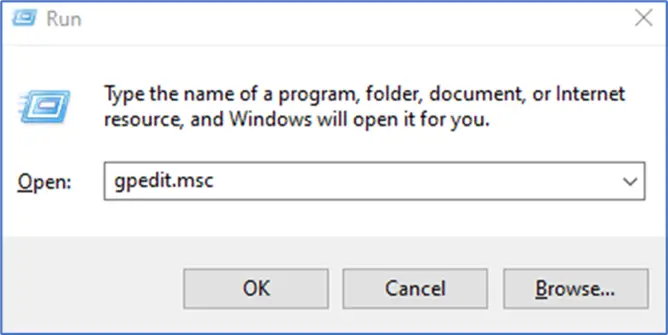
Quick technology tips and tricks article to explain how to allow multiple RDP sessions on a Windows machine.
Project Responsibilities
This page details the responsibilities for a project
What Sets Secure Ideas Apart From Other Security Consulting Firms?
This page outlines Secure Ideas’ experience and expertise in the field of information security