
In Case of Fire: Break Windows
When a client calls us to pentest a web application that is only available in Internet Explorer. I cringe. I don’t know if it’s flashbacks from…
Better API Penetration Testing with Postman – Part 4
This is the final part of this series. We will use some of Burp Suite’s extensions to augment your API testing toolchain.
Better API Penetration Testing with Postman – Part 3
We will dig into some slightly more advanced functionality in Postman that you almost certainly want to leverage.
Better API Penetration Testing with Postman – Part 2
In Part 1 of this series, I walked through an introduction to Postman, a popular tool for API developers that makes it easier to test API calls.
Better API Penetration Testing with Postman – Part 1
This is the first of a multi-part series on testing with Postman.
Introduction to Wireless Security with Aircrack-ng

Today we’re going to walk through a few WiFi testing examples using Aircrack-ng, which is a suite of wireless network security tools.
Finding Your Weakness: Triaging Your Domains with SWAT
One of the common issues in IT and security is having a handle on what all of the domains are doing and how they are maintained.
Tips for Penetration Testing a PCI environment
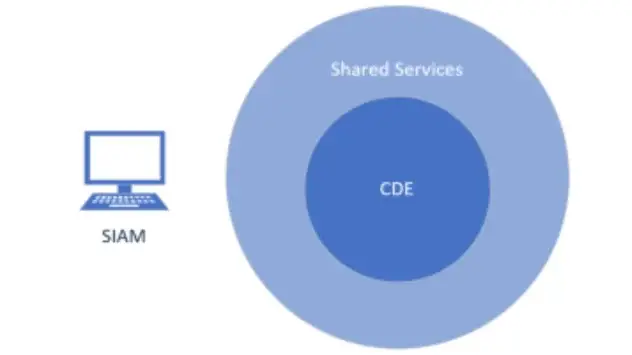
A list of things to help me keep my PCI testing on track, not to mention just as a guideline to start discussions among others doing similar testing.
The Report
Being a pen tester is a cool job, we get to break into companies (with permission), steal stuff, and then tell them how we did it.
Ever Run a Relay? Why SMB Relays Should Be On Your Mind
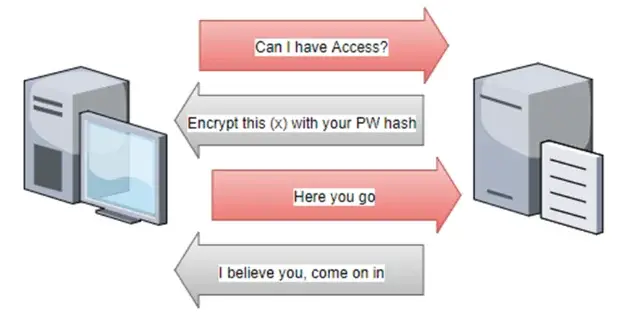
Time is never on your side when you’re onsite with a client and trying to get the first good foothold, with admin privileges, can seem impossible.