
Extract Secrets from Multiple Configuration Files Using Vim
Learn how to extract secrets from compromised Linux servers using Vim’s built-in capabilities. This guide shows penetration testers how to search config files, extract credentials, and exfiltrate data without leaving forensic artifacts.
No Broadcast Traffic? No Problem! – NetExec SMB Slinky Module
Explore how the Slinky SMB module in NetExec can capture NTLM hashes and conduct relay attacks in environments without broadcast traffic.
Red Team vs. Purple Team: What’s the difference?
Explore Red Team vs Purple Team to strengthen your organization’s cybersecurity through targeted testing and collaboration.
Proxies, Pivots, and Tunnels – Oh My!
Talking about a proxy or a pivot or a tunnel, we could be talking about very different things. However, to me, these terms could mean the same thing too.
Automating Red Team Homelabs: Part 1 – Kali Automation
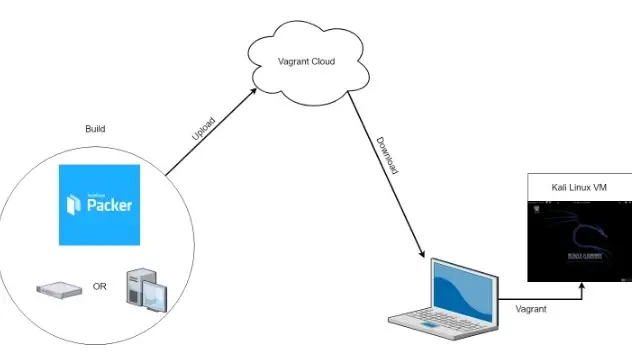
Part 2: /2019/05/automating-red-team-homelabs-part-2-build-pentest-destroy-and-repeat.html Homelab infrastructure got you down?
Red Teaming – Not What You May Have Thought
I’ve been doing a lot of reading on some less technical topics and I ran across “Red Team: How to Succeed By Thinking Like the Enemy” by Micah Zenko.
Comprehensive Testing: Red and Blue Make Purple Webcast

James Jardine and I held the Comprehensive Testing (Purple Teaming) webcast yesterday.