
The Critical Need for API Security Testing
Discover why API security testing is crucial for protecting sensitive data and preventing breaches in modern applications.
How much does a Penetration Test Cost?
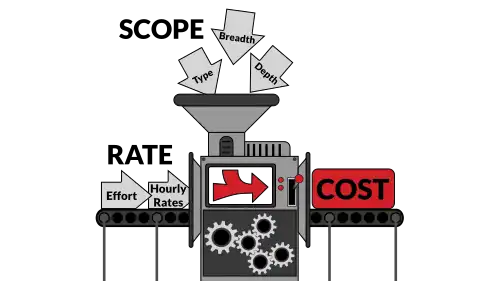
This article describes what the cost of a penetration test from Secure Ideas is, as well as ways to affect the final bill.
What is a Threat-Led Penetration Test?
Explore Secure Ideas’ expert approach to Threat-Led Pen Testing (TLPT) and proactive cybersecurity strategies.
Does Time Boxed Pentesting Have Value?
Discover the efficiency of time-boxed penetration testing. Maximize coverage, complement ongoing testing, and address security challenges effectively.
Mission Imfuzzable: How to Fuzz Web Apps you can’t Intercept
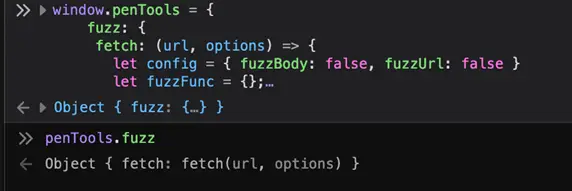
This post deals with a real-world scenario of testing a web app that could not be intercepted, and the tooling that came from the solving that.
Finding Your Spidey Sense
As you begin your web app pentesting adventure, it’s essential to understand the treacherous landscape you’re about to explore.
Understanding Server-Side Template Injection (SSTI)
Discover the risks of Server-Side Template Injection (SSTI) vulnerabilities, learn how to detect and prevent them, and safeguard your web applications.
Introducing SamuraiWTF 5.3: A Powerhouse for Web App Pen Testing
Explore SamuraiWTF 5.3, the latest in web application penetration testing. New updates to Katana offer enhanced tools for a robust security toolkit.
Secure Ideas Penetration Testing Process: A Comprehensive Overview
This page discusses the processes followed during a penetration test
What is a Penetration Test and Why is it Important?
This article explains the concept of a penetration test and why it is important that organizations perform penetration testing.