
Silencing Firefox’s Chattiness for Web App Testing
Firefox is one chatty browser! Even if you don’t actually use it for anything, it’s constantly making requests out to the internet for things.
Tips for Penetration Testing a PCI environment
A list of things to help me keep my PCI testing on track, not to mention just as a guideline to start discussions among others doing similar testing.
Going the distance with Burp
Welcome to the 5th blog on Burp Suite, and Happy 4th of July!
Burp Suite continuing the Saga
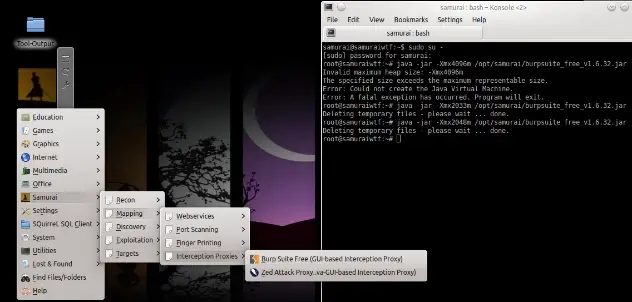
Welcome to the fourth blog introducing and exploring the features of Burp Suite. Please visit Secure Ideas’ previous blogs on using Burp Suite
SQLMap Beginnings: What and How
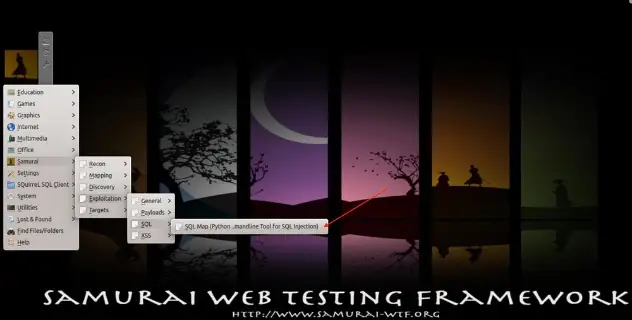
Testing web based applications is not only fun but is often multi-faceted and challenging. Often times a web front end will have places for data input.
Tip: Running BurpSuite on a Mac
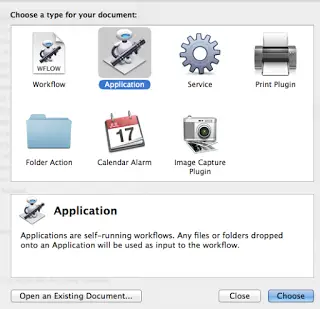
Quick tip to save some time when spinning up Burp Suite on a Mac. Use Burp Suite frequently enough that having an icon on my task bar is warranted.
Web App Pre-Flight
I think that it is because of my background in software development that I am passionate about integrating security testing with the SDLC.
SIAM: Custom Testing Machines
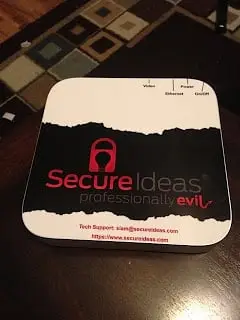
Secure Ideas recently made the decision to create custom machines that we could use for penetration testing engagements.
Comparing Authorization Levels with Burp’s Compare Site Map feature
Burp Suite from Portswigger.net is a fantastic web app testing tool that we use regularly at Secure Ideas.
Why Do Phishing As Part of Security Testing

I was recently watching a web cast on incident response and found myself thinking about the cause of the example incident.