
Silencing Firefox’s Chattiness for Web App Testing
Firefox is one chatty browser! Even if you don’t actually use it for anything, it’s constantly making requests out to the internet for things.
Three C-Words of Web App Security: Part 1 – CORS
For those less versed in web applications and how they’ve evolved, I wrote a sort of prologue to this post back in April 2018.
Going the distance with Burp
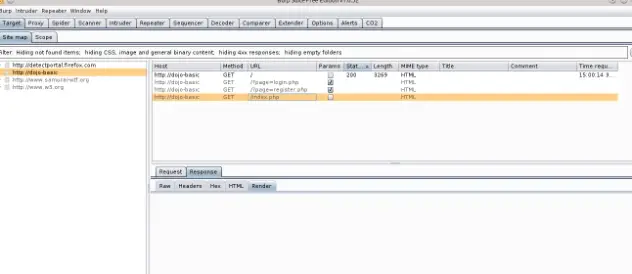
Welcome to the 5th blog on Burp Suite, and Happy 4th of July!
Burp Suite continuing the Saga
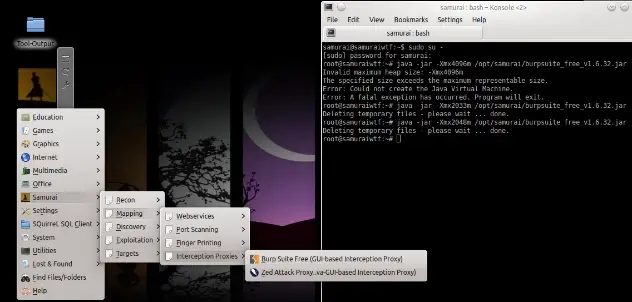
Welcome to the fourth blog introducing and exploring the features of Burp Suite. Please visit Secure Ideas’ previous blogs on using Burp Suite
SQLMap Beginnings: What and How
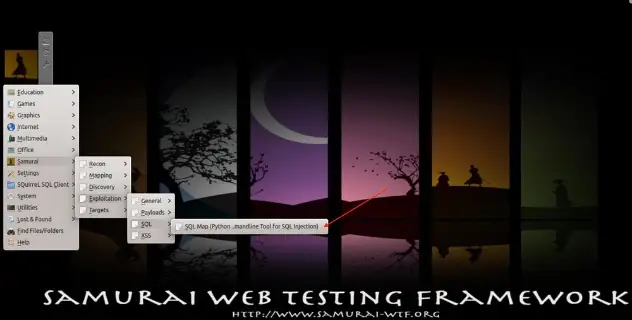
Testing web based applications is not only fun but is often multi-faceted and challenging. Often times a web front end will have places for data input.
CORS Global Policy

I recently noticed an uptake on Cross-Origin Resource Sharing (CORS) findings showing up in automated scanning tools…
Scary Web Services: Part 2
Although Snapchat’s breach appears to be due to some poor assumptions around an “internal” Snapchat API, it is not the type of traditional web service…
Scary Web Services: Part 1
I have several things I want to say about web services but why are web services scary to me in the role of a pen tester?
Web App Pre-Flight
I think that it is because of my background in software development that I am passionate about integrating security testing with the SDLC.
We Can’t Rely on the Browser for Protection
A large part of doing security consulting is providing proper mitigations and recommendations to our clients. Sure, the testing is the exciting part…