
Quick Bites Ep 4 – Let’s Talk About SSRF, Baby!
This Quick Bites will help you gain a basic understanding of SSRF, how it’s exploited, and how to mitigate it.
How to Obfuscate Strings in Rust the Easy Way Using the litcrypt Crate
How to accomplish string obfuscation in Rust the easy way using the litcrypt crate.
Application Security 202: Vulnerabilities Accepted

Studying how to accept vulnerabilities and secure applications
(Not So) Quick Bites – Episode 3 – Writing About Writer’s Block
On this (Not So) Quick Bites, we’re talking about writer’s block, and how to get over it. Here’s five tips and tricks that I use to get to writing.
Hunting Secrets
A rundown of the Secrets Hunter capability within Paramalyzer, used to quickly find instances of sensitive information leakage in web applications.
Ensuring Web Security via Ansible (Apache)
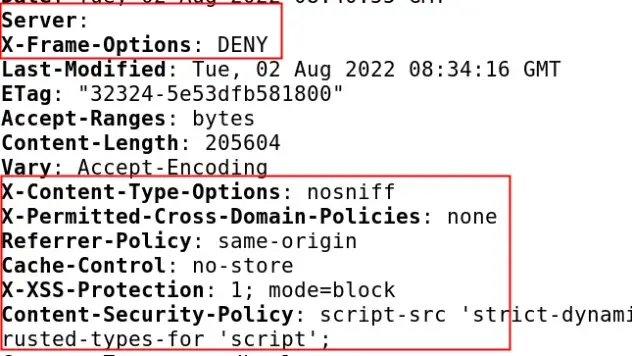
Using ansible to add security headers to an apache web server (idea), environment defined in a Vagrantfile
Application Security 101
Application security is a big job, for sure. And it’s not just the job of the developers or the SOC. There is an incredible amount of surface to cover.
Why your application needs a Content Security Policy (And How to Build One)
This post outlines the importance of building a content security policy (CSP) to secure web applications, and how to get started building one.
Quick Bites Episode 2 – HTTP Security Headers and Why You NEED Them
Secure Ideas’ Quick Bites Ep 2 – HTTP security headers are important for webapp security. Here are some that will help lockdown your site a little better.
Privilege Escalation via File Descriptors in Privileged Binaries
Post on SetUID drop-privileges binaries with leaked file descriptors, allowing for PrivEsc. Covers how to exploit & a tool to streamline exploitation.