
LD_PRELOAD: Making a Backdoor by Hijacking accept()
A demonstration on how to use LD_PRELOAD to create a backdoor in processes by hooking the accept() function.
Digging Between the Couch Cushions – CouchDB CVE-2021-38295 Breakdown
In this blog post we’re going to take a look at the recent CouchDB vulnerability, CVE-2021-38295, which I was credited with discovering.
AppSec Cheat Code: Shift Left, Shift Right, Up, Down & Start
Seamless and unobtrusive security is the future. We are huge advocates of shifting left and moving security testing earlier in the development process.
Three Excellent API Security Practices Most People Neglect
Widely-used single-purpose products like Slack to cloud-based solutions like AWS and Microsoft Azure, APIs are used to drive business processes.
How to configure Android (Virtual) for Mobile PenTest
This post is about setting up an Android Virtual Machine (AVD) for a mobile application penetration test.
Waving the White Flag: Why InfoSec should stop caring about HTTPOnly
As a company that is constantly working with our penetration testing clients on understanding where they should focus their efforts…
Proxying HTTPS Traffic with Burp Suite
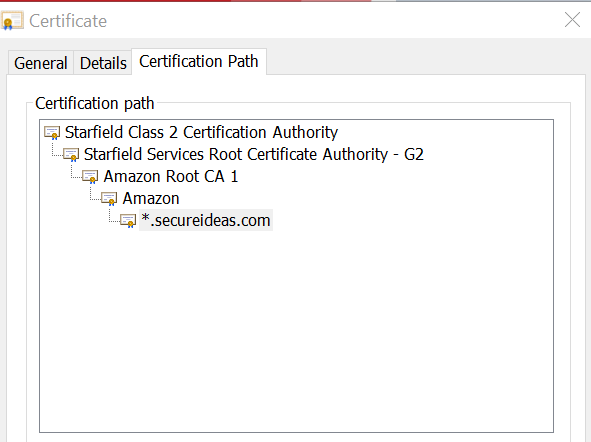
Because every new installation of Burp generates a different CA, this doesn’t create a risk of somebody else intercepting your traffic surreptitiously.
Getting Started API Penetration Testing with Insomnia
In our blog series on Better API Penetration Testing with Postman we discussed using Postman as the client for testing RESTful service APIs.
How I Became a Security Consultant: AbsoluteAppsec Interview
Every so often, podcasts and such will invite me to speak on a variety of topics. And this week, I was very excited to join @cktricky and @sethlaw…
Once upon a time there was a WebSocket
This is the story from one of our recent penetration testing engagements.