PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Password Vampires: Don’t Get Bitten Twice

With Halloween right around the corner, let’s talk about your dark secret from the distant past that could really come back to haunt you: that password you’ve been using since 2015. Don’t lie… You know the one.

...

All Entries

Network Check Ups

Network Check Ups

Most people know that taking care of your personal health is important. We get regular check ups and try to keep ourselves as healthy as...
Compliance is not Security

Compliance is not Security

Many folks get confused about the difference between security and compliance. Many, especially those less technically inclined, assume that fulfilling......
Three C Words of Web App Security: Part 2 – CSRF

Three C-Words of Web App Security: Part 2 – CSRF

I identified several types of requests as generally considered safer, and therefore not subject to CORS when being sent across origins....
SamuraiWTF

SamuraiWTF 4.0 Finally Released

As we discussed previously, the build process that has supported this project for the last decade is WAY too difficult to maintain....
Silencing Firefox's Chattiness for Web App Testing

Silencing Firefox’s Chattiness for Web App Testing

Firefox is one chatty browser! Even if you don’t actually use it for anything, it’s constantly making requests out to the internet for things....
Not Just Another Notch in Your Belt: Organizational Challenges of PCI Compliance

Not Just Another Notch in Your Belt: Organizational Challenges of PCI Compliance

Questions surrounding PCI compliance and the challenges organizations face with ensuring proper controls are in place, and all requirements met....
Automating Red Team Homelabs: Part 1 Kali Automation

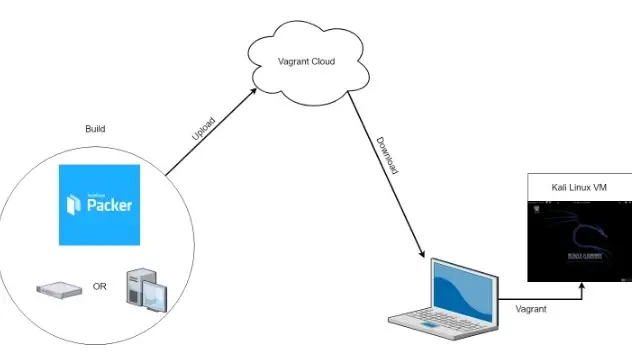
Automating Red Team Homelabs: Part 1 – Kali Automation

Part 2: /2019/05/automating-red-team-homelabs-part-2-build-pentest-destroy-and-repeat.html Homelab infrastructure got you down?...
Still SMiShing You SMS Scams.

Still SMiShing You – SMS Scams.

Have you ever gotten a strange text message on your phone that you don’t recognize? Well, be careful because you don’t have to use a...
default

Introduction to Wireless Security with Aircrack-ng

Today we’re going to walk through a few WiFi testing examples using Aircrack-ng, which is a suite of wireless network security tools....
Escaping the Whale: Things You Probably Shouldn’t Do With Docker (part 2)

Escaping the Whale: Things You Probably Shouldn’t Do With Docker (part 2)

This post is part 2 of a series of blog posts on container hacking. If you haven’t read the part1, you should check it out....
Triaging Your Domains with SWAT

Finding Your Weakness: Triaging Your Domains with SWAT

One of the common issues in IT and security is having a handle on what all of the domains are doing and how they are...
Tips for Penetration Testing a PCI environment

Tips for Penetration Testing a PCI environment

A list of things to help me keep my PCI testing on track, not to mention just as a guideline to start discussions among others...

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy.