PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Password Vampires: Don’t Get Bitten Twice

With Halloween right around the corner, let’s talk about your dark secret from the distant past that could really come back to haunt you: that password you’ve been using since 2015. Don’t lie… You know the one.

...

All Entries

Ransomware and Scareware Pop ups

Ransomware and Scareware Pop-ups

Every computer owner has had the heart-stopping moment where a popup comes up and says that your computer has been infected....
Targeted Pineapple Setup (7 easy steps to gather credentials onsite)

Targeted Pineapple Setup (7 easy steps to gather credentials onsite)

The WiFi Pineapple Tetra is a wireless auditing tool from Hak5 that simplifies and automates the process of performing many wireless attacks....
Are You Ready for Your Pen Test?

Are You Ready for Your Pen Test?

It is day three of a five-day penetration test engagement and we still don’t have all the information we need to proceed with the test....
Ransomware Intelligence Briefing

Ransomware Intelligence Briefing

Ransomware Intelligence Briefing Media reporting on the WannaCry ransomware campaign has contained exaggeration, bad information, and fear tactics....
Protecting your Kids from Online Threats

Protecting your Kids from Online Threats

As information security professionals, we’re often asked about how to best protect children online....
An Introduction to Javascript for XSS Payloads

An Introduction to Javascript for XSS Payloads

I recently got the opportunity to speak at B-Sides Charleston on cross-site scripting (XSS) payload development....
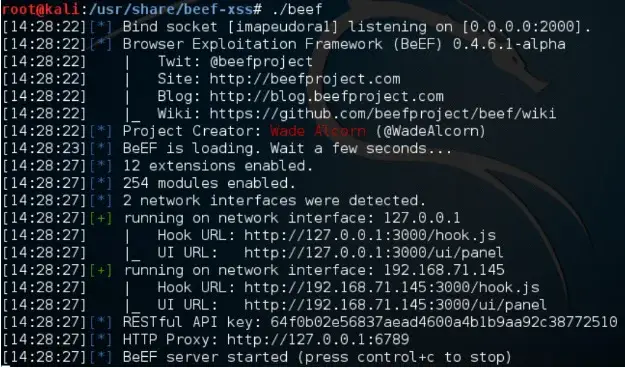
A Brief BeEF Overview

A Brief BeEF Overview

BeEF, the Browser Exploitation Framework, is a testing tool that allows the penetration tester to look past hardened network perimeter and client system.....
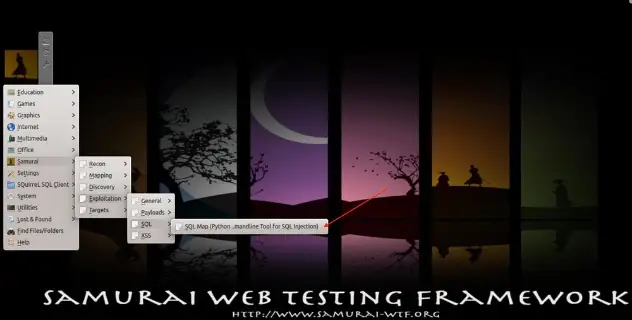
SQLMap Beginnings: What and How

SQLMap Beginnings: What and How

Testing web based applications is not only fun but is often multi-faceted and challenging. Often times a web front end will have places for data...
Reversing Type 7 Cisco Passwords

Reversing Type 7 Cisco Passwords

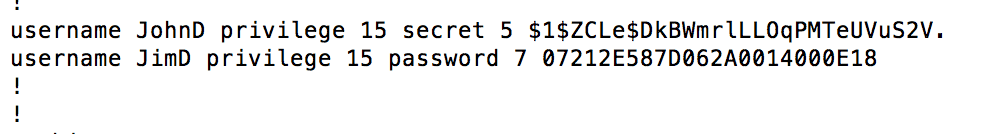
While working on a recent pen test, I came across a few Cisco routers sitting on an internal network......
default

We’re Just Like the NSA, and Nothing Like Them

During penetration tests, and especially scoping calls, we often get quizzed about what secret, proprietary techniques we’ll use......
Red Teaming Not What You May Have Thought

Red Teaming – Not What You May Have Thought

I’ve been doing a lot of reading on some less technical topics and I ran across “Red Team: How to Succeed By Thinking Like the...
Five Outdated Security Excuses

Five Outdated Security Excuses

The Security Industry as a whole has been known to criticize businesses large and small with respect to how they manage security....

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy.