PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Password Vampires: Don’t Get Bitten Twice

With Halloween right around the corner, let’s talk about your dark secret from the distant past that could really come back to haunt you: that password you’ve been using since 2015. Don’t lie… You know the one.

...

All Entries

Red Dawn: Protecting small organizations from attacks

Red Dawn: Protecting small organizations from attacks

We work with organizations both large and small and help people trying to figure out what the threats and risks are in the wild today....
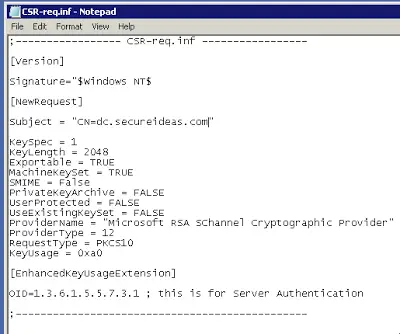
Creating SSL Certificate Requests Using Certreq.exe and Enable LDAPS

Creating SSL Certificate Requests Using Certreq.exe and Enable LDAPS

This post picks up on my last about creating and authorizing an internal certificate authority....
Your Passwords Were Stolen: What's Your Plan?

Your Passwords Were Stolen: What’s Your Plan?

If you have been glancing at many news stories this year, you have certainly seen the large number of data breaches that have occurred....
SSL Certificates: Setting Up and Authorizing the Internal Certificate Authority

SSL Certificates: Setting Up and Authorizing the Internal Certificate Authority

In this post, I wanted to give something directly to the Blue Teams out there....
Using a Throwing Star to Capture Packets

Using a Throwing Star to Capture Packets

Mobile applications are a hot commodity these days. It seems like everyone and their brother/sister is writing them....
default

Preparing for a Consultant

As security consultants, we regularly travel to clients’ sites and experience a wide range of environments and atmospheres....
default

Autocomplete and actual risk: Why do we look at it?

Autocomplete is always a fun topic to discuss…. ok maybe my idea of fun is not the normal idea. 🙂...
Professionally Evil: This is NOT the Wireless Access Point You are Looking For

Professionally Evil: This is NOT the Wireless Access Point You are Looking For

I was recently conducting a wireless penetration test and was somewhat disappointed to find that they had a pretty well configured set of wireless networks...
Professionally Evil: Your Stealth Startup is Showing

Professionally Evil: Your Stealth Startup is Showing

During our penetration tests we often get asked about the amount of information that is leaking out via social networks, web pages and the like....
default

Brute Forcing the Change Password Feature

As a penetration tester, brute force attacks are something I test for on every application....
default

GSA Database May Have Leaked Information: Kevin Johnson was Interviewed

It was announced that there was a security flaw found in one of the GSA systems that could have allowed for vendors to see other...
default

Hiring Philosophy and How to Get Into InfoSec

As one of the founders of Secure Ideas, I am often asked how someone gets into InfoSec and/or how do they get hired at Secure...

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy.