PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Password Vampires: Don’t Get Bitten Twice

With Halloween right around the corner, let’s talk about your dark secret from the distant past that could really come back to haunt you: that password you’ve been using since 2015. Don’t lie… You know the one.

...

All Entries

default

Scary Web Services: Part 2

Although Snapchat’s breach appears to be due to some poor assumptions around an “internal” Snapchat API, it is not the type of traditional web service......
Intercepting DNS

Intercepting DNS

Recently during a penetration test, I discovered a Linksys WRT54G wireless router that had been installed on a customer’s network....
default

Professionally Evil Software: Laudanum 1.0 release!

Secure Ideas is excited to announce the immediate release of Laudanum 1.0....
default

Why Target’s Breach Included PIN Data

Last Friday Target issued an update acknowledging that encrypted PIN data were included in the data stolen in their recent breach....
default

Target Security Breached: What You Need to Know

All it takes is one big nasty security breach and the whole world will be watching you through a microscope....

Password Sharing Across Accounts

Over the past few years we have seen a large number of databases get compromised leading to the disclosure of user passwords....

Scary Web Services: Part 1

I have several things I want to say about web services but why are web services scary to me in the role of a pen...
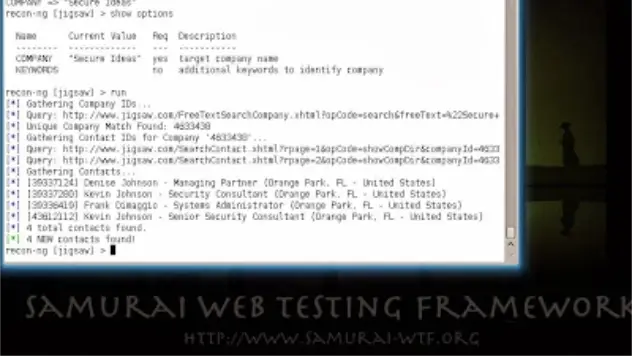
Professionally Evil Toolkit Recon ng

Professionally Evil Toolkit – Recon-ng

The first stage of almost every successful penetration test is the reconnaissance phase. During this phase of an engagement we scour publicly accessible......

Web App Pre-Flight

I think that it is because of my background in software development that I am passionate about integrating security testing with the SDLC....
default

Security Tubthumping

I have a friend who is an alcoholic. A few weeks ago after 5 years of sobriety, she stumbled and had a relapse....
default

Professionally Evil: Self Inflicted Injury at Vendor’s Request

It’s an unfortunate and still too common a vulnerability to find administrative interfaces exposed and configured with default passwords....
SIAM: Custom Testing Machines

SIAM: Custom Testing Machines

Secure Ideas recently made the decision to create custom machines that we could use for penetration testing engagements....

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy.