PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Password Vampires: Don’t Get Bitten Twice

With Halloween right around the corner, let’s talk about your dark secret from the distant past that could really come back to haunt you: that password you’ve been using since 2015. Don’t lie… You know the one.

...

All Entries

Evaluating AI Language Tutors Through a Security Lens

Evaluating AI Language Tutors Through a Security Lens

Evaluating the security risks of AI language tutors, exploring how personal data collected can be exploited, and offering practical steps for safer use....
What factors impact the cost of Reporting

What factors impact the cost of Reporting?

This article outlines the main factors that impact the effort and cost of the reporting phase of a penetration test engagement....
Rolling for Resilience Part 3: Battle Prep The Scrolls of Response

Rolling for Resilience Part 3: Battle Prep – The Scrolls of Response

Part three focuses on Playbooks. Understanding their purpose, importance, and responsibilities to review and keep them updated....
Paths to Power in Active Directory Part 2: ESC1 – No One, Yet Anyone

Paths to Power in Active Directory Part 2: ESC1 – No One, Yet Anyone

Learn how to exploit AD CS misconfigurations for privilege escalation from a low-privileged user to Domain Admin in Active Directory....
What is GLBA Compliance Penetration Testing?

What is GLBA Compliance Penetration Testing?

This article describes what is included in GLBA Compliance Penetration Testing and how it helps educational organizations meet GLBA obligations....
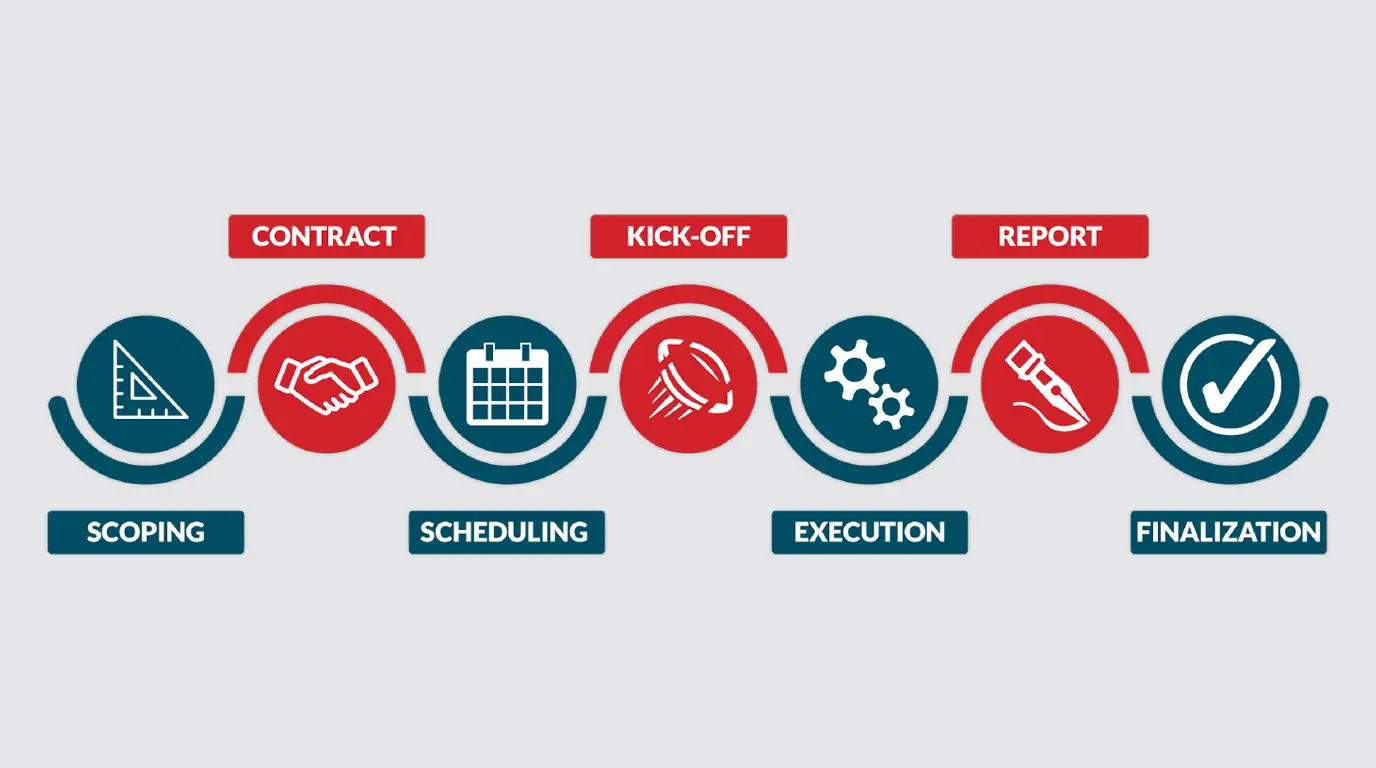
What is the Secure Ideas engagement process

What is the Secure Ideas engagement process?

This article describes the main steps in the process for engaging Secure Ideas for penetration testing and consulting services....
Extract Secrets from Multiple Configuration Files Using Vim

Extract Secrets from Multiple Configuration Files Using Vim

Learn how to extract secrets from compromised Linux servers using Vim's built-in capabilities. This guide shows penetration testers how to search config files, extract credentials,...
What are the Tools and Rules of Engagement at Secure Ideas for Web Application Penetration Tests

What are the Tools and Rules of Engagement at Secure Ideas for Web Application Penetration Tests?

Our clients often ask about the specific tools we use during a pen-test and the rules of engagement we adhere to ensure the security and...
Paths to Power in Active Directory Part 1: How AD CS Misconfigurations Become the Keys to the Kingdom

Paths to Power in Active Directory Part 1: How AD CS Misconfigurations Become the Keys to the Kingdom

From regular domain user to Domain Admin in minutes. Discover how AD CS misconfigurations create one of Active Directory's most abusable attack paths....
No Broadcast Traffic? No Problem! NetExec SMB Slinky Module

No Broadcast Traffic? No Problem! – NetExec SMB Slinky Module

Explore how the Slinky SMB module in NetExec can capture NTLM hashes and conduct relay attacks in environments without broadcast traffic....
Annual Pentests Aren't Cutting It Anymore: Why Continuous Testing Beats Scrambling at Renewal Time

Annual Pentests Aren’t Cutting It Anymore: Why Continuous Testing Beats Scrambling at Renewal Time

From annual fire drill to continuous security: Why PCI DSS, HIPAA, and cyber insurance requirements are pushing organizations toward ongoing testing....
Quantum Leaping Through Data: Preparing for the Quantum Encryption Transition

Quantum Leaping Through Data: Preparing for the Quantum Encryption Transition

Quantum computers will break current encryption within 10 years, but adversaries are harvesting your data today. Your migration window is narrower than you think....

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy.