PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Compiling is Not Hiding: Hardcoded Secrets in Mobile Apps

Most of the secrets I’ve found in mobile apps were not stolen. They were shipped. What do I mean by that? I mean nobody needs to break into the vault when the combination is printed on every door. Compiling is not hiding: it changes the format of the code, not...

All Entries

Cybersecurity Essentials for SMBs: Building a Robust Program

Cybersecurity Essentials for SMBs: Building a Robust Program

Learn how SMBs can build a robust cybersecurity program by focusing on essential steps, roles, and strategies to safeguard their business and customers....
The Essential Eight

The Essential Eight

Explore how the Australian Signals Directorate’s Essential 8 cybersecurity controls compare to the NIST 800-53 framework....
From Nmap to CSV

From Nmap to CSV

Streamline Nmap data analysis with a bash script that converts output to a CSV format, optimizing penetration testing and improving communication with stakeholders....
You Don’t Need PKINIT To Win It

You Don’t Need PKINIT To Win It

Explore LDAP privilege escalation in pentests using Certipy's ldap-shell. Learn how to bypass PKINIT issues and escalate privileges with advanced techniques....
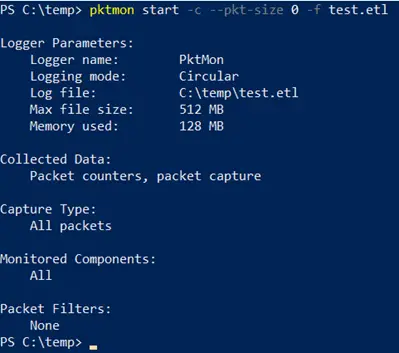
Built In Network Capture with Windows 11

Built-In Network Capture with Windows 11

Discover how to utilize Windows 11's built-in network packet capture utility, pktmon, for efficient network traffic analysis without additional software....
Running and Debugging Non native ELF Binaries

Running and Debugging Non-native ELF Binaries Locally Using QEMU, BINFMT, and GDB

This is a blog that explains how to use QEMU + BINFMT + GDB to run and debug non-native ELF binaries extracted from firmwares locally...
Who Really Owns Your Data?

Who Really Owns Your Data?

Exploring the erosion of consumer ownership and privacy through the digital age with examples from Amazon Kindle, Bambu Labs, and 23andMe....
When Algorithms Aren’t Enough

When Algorithms Aren’t Enough: Why the Human Element Still Matters in Modern Penetration Testing

Discover why human expertise is crucial in penetration testing and how it surpasses automated tools in delivering comprehensive security insights....
The Invisible World in Motion

OT: The Invisible World in Motion

Discover the essential role of Operational Technology (OT) in everyday life and its intersection with IT, from smart homes to industrial environments and amusement parks....
Solicited Public Comment on HIPAA Security Rule NPRM To Strengthen the Cybersecurity of ePHI

Solicited Public Comment on HIPAA Security Rule NPRM To Strengthen the Cybersecurity of ePHI

Explore challenges in the proposed HIPAA Security Rule, including underestimating penetration testing costs and time for small to medium-sized healthcare providers....
Building a Custom Burp Suite Collaborator Everywhere BApp

Building a Custom Burp Suite Collaborator Everywhere BApp

Learn how to customize Burp Suite's Collaborator Everywhere BApp using Docker and Gradle for better compatibility with your client's web applications....
Quick Bites

Quick Bites Episode 12 – Hidden Treasures

Discover the thrill of penetration testing as Aaron Moss uncovers a unique XSS vulnerability, emphasizing the importance of sanitizing all inputs in web applications....

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy