PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Compiling is Not Hiding: Hardcoded Secrets in Mobile Apps

Most of the secrets I’ve found in mobile apps were not stolen. They were shipped. What do I mean by that? I mean nobody needs to break into the vault when the combination is printed on every door. Compiling is not hiding: it changes the format of the code, not...

All Entries

Operational Technology’s use of Wireless Networks

Operational Technology’s use of Wireless Networks

Explore the evolving role of wireless networks in Operational Technology, the challenges they present, and the importance of regular configuration reviews....
How to Get the Most Out of Your Penetration Test: A Guide to Preparation and Success

How to Get the Most Out of Your Penetration Test: A Guide to Preparation and Success

Learn how proper preparation ensures a successful penetration test. Discover key steps like access management for a thorough security assessment....
When Security Fails: What The DeepSeek Incident Can Teach Us About AI Security

When Security Fails: What The DeepSeek Incident Can Teach Us About AI Security

Learn how the DeepSeek incident highlights critical AI security challenges and discover best practices for protecting AI applications from emerging threats....
Navigating the Security Roadmap: TISAX for Automotive OEMs

Navigating the Security Roadmap: TISAX for Automotive OEMs

Learn how OEMs can strengthen security with TISAX compliance and PETaaS®, driving innovation while protecting their supply chain and brand trust....
Countdown to Full Compliance: PCI DSS 4.0.1

Countdown to Full Compliance: PCI-DSS 4.0.1

Get ready for the PCI DSS v4.0.1 compliance deadline by addressing key requirements like multi-factor authentication, malware scanning, and automated audit log reviews....
Best Practices and Risks Considerations in Automation like LCNC and RPA

Best Practices and Risks Considerations in Automation like LCNC and RPA

Best practices and risk considerations in using Low-Code/No-Code (LCNC) and Robotic Process Automation (RPA) for digital transformation and automation....
Understanding TISAX: Securing the Path Forward for Automotive Innovation

Understanding TISAX: Securing the Path Forward for Automotive Innovation

Learn about TISAX, the trusted assessment and framework for securing automotive industry data....
The Critical Need for API Security Testing

The Critical Need for API Security Testing

Discover why API security testing is crucial for protecting sensitive data and preventing breaches in modern applications....
Stay safe from cybercrime with these five tips

Stay safe from cybercrime with these five tips

Stay safe from cybercrime with five essential cybersecurity tips, including using multi-factor authentication, keeping software updated, and security training for employees....
Red Team vs. Purple Team: What's the difference?

Red Team vs. Purple Team: What’s the difference?

Explore Red Team vs Purple Team to strengthen your organization's cybersecurity through targeted testing and collaboration....
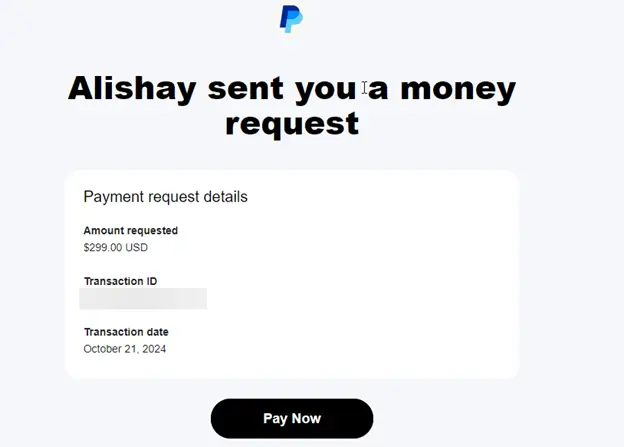
The Fellowship of the Phish: PayPal's Perilous Request Feature

The Fellowship of the Phish: PayPal’s Perilous Request Feature

Discover how attackers exploit legitimate features in PayPal's system to execute sophisticated phishing scams and what we can learn from creative misuse....
Secure Ideas is CREST Certified. Here’s Why That Matters

Secure Ideas is CREST-Certified. Here’s Why That Matters

Confidence in penetration testing suppliers comes with credentials. We're proud to hold CREST certification....

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy