
Detecting Dangling SaaS Subdomains and Real Subdomain Takeovers
Detecting and mitigating dangling SaaS subdomains and real subdomain takeovers with a more accurate, reliable tool to reduce false positives and build trust in security assessments.
AI Agents: Clippy With Root Access
AI agents are transforming productivity but pose serious security risks. Secure their access & treat them as high-risk systems to avoid potential breaches.
What factors impact the cost of Reporting?
This article outlines the main factors that impact the effort and cost of the reporting phase of a penetration test engagement.
Paths to Power in Active Directory Part 2: ESC1 – No One, Yet Anyone
Learn how to exploit AD CS misconfigurations for privilege escalation from a low-privileged user to Domain Admin in Active Directory.
What is GLBA Compliance Penetration Testing?
This article describes what is included in GLBA Compliance Penetration Testing and how it helps educational organizations meet GLBA obligations.
What is the Secure Ideas engagement process?
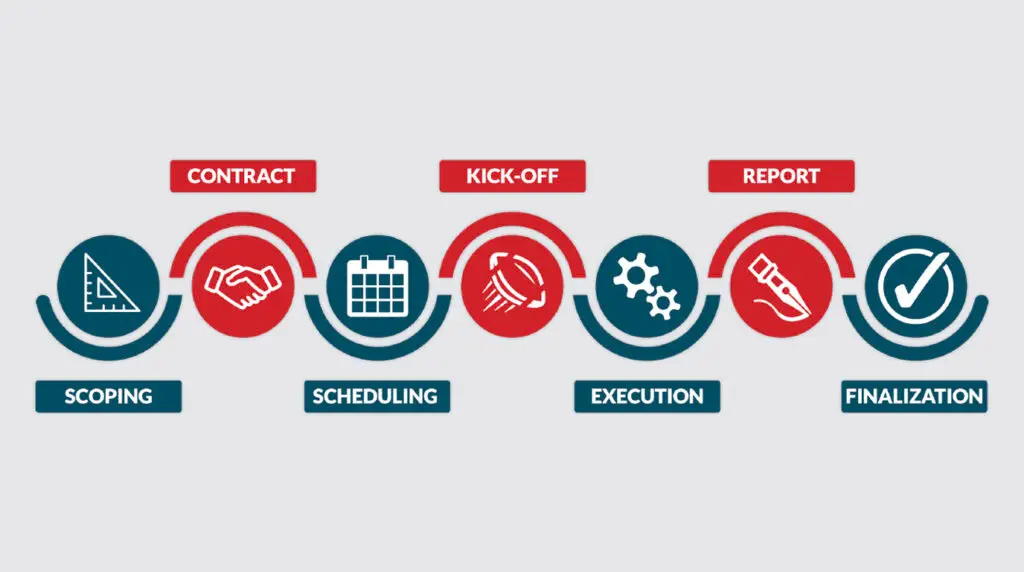
This article describes the main steps in the process for engaging Secure Ideas for penetration testing and consulting services.
Extract Secrets from Multiple Configuration Files Using Vim
Learn how to extract secrets from compromised Linux servers using Vim’s built-in capabilities. This guide shows penetration testers how to search config files, extract credentials, and exfiltrate data without leaving forensic artifacts.
What are the Tools and Rules of Engagement at Secure Ideas for Web Application Penetration Tests?
Our clients often ask about the specific tools we use during a pen-test and the rules of engagement we adhere to ensure the security and integrity of their applications. This article aims to address these concerns, providing an in-depth understanding
Paths to Power in Active Directory Part 1: How AD CS Misconfigurations Become the Keys to the Kingdom
From regular domain user to Domain Admin in minutes. Discover how AD CS misconfigurations create one of Active Directory’s most abusable attack paths.
No Broadcast Traffic? No Problem! – NetExec SMB Slinky Module
Explore how the Slinky SMB module in NetExec can capture NTLM hashes and conduct relay attacks in environments without broadcast traffic.