
Annual Pentests Aren’t Cutting It Anymore: Why Continuous Testing Beats Scrambling at Renewal Time
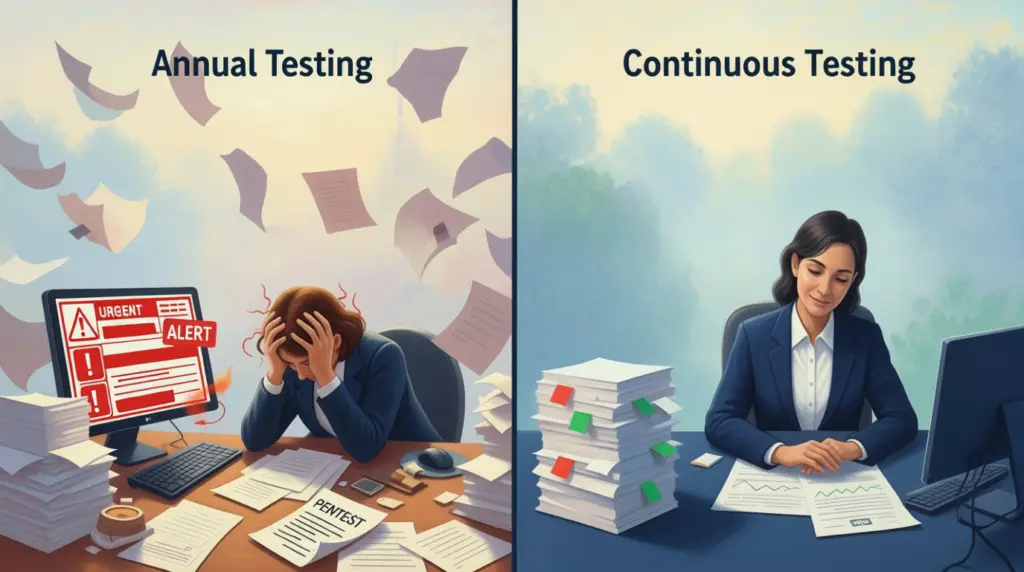
From annual fire drill to continuous security: Why PCI DSS, HIPAA, and cyber insurance requirements are pushing organizations toward ongoing testing.
The Real AI Revolution in Penetration Testing
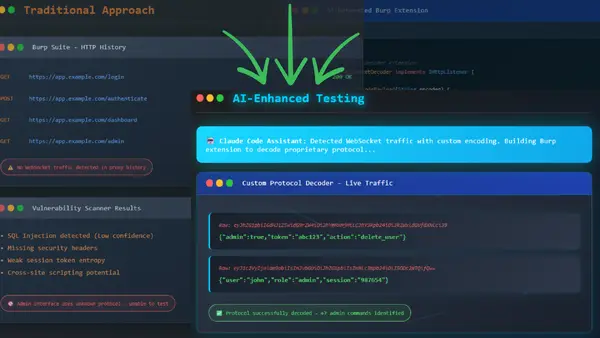
AI-powered custom exploit development & penetration testing for complex protocols. Professional assessments in hours, not days.
Quick Bites 13 – Network Pentest Restrictions Can Hurt Your Business
Explore the importance of proper scoping in network penetration testing, the risks of over-restricting tests, and how to ensure meaningful security outcomes.
Risk-Driven Approach: The Federal Government’s Shift in Cybersecurity Burden
Explore the shift from all-hazards to risk-informed security testing. Learn how Threat-Led and Assumed Breach testing support the new risk-informed paradigm.
Understanding Garbage Findings
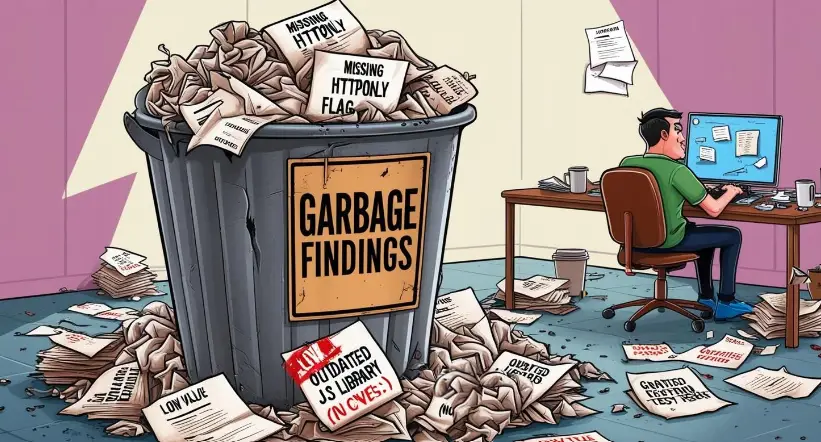
Learn how to identify garbage findings in penetration testing reports by evaluating real risk, impact, and conditions in application security assessments.
Houston, We Have a Problem
Discover how comprehensive satellite penetration testing addresses vulnerabilities across spacecrafts, ground systems, and communication links to ensure end-to-end cybersecurity in space operations.
When Algorithms Aren’t Enough: Why the Human Element Still Matters in Modern Penetration Testing
Discover why human expertise is crucial in penetration testing and how it surpasses automated tools in delivering comprehensive security insights.
Solicited Public Comment on HIPAA Security Rule NPRM To Strengthen the Cybersecurity of ePHI
Explore challenges in the proposed HIPAA Security Rule, including underestimating penetration testing costs and time for small to medium-sized healthcare providers.
How to Get the Most Out of Your Penetration Test: A Guide to Preparation and Success
Learn how proper preparation ensures a successful penetration test. Discover key steps like access management for a thorough security assessment.
The CISO’s Myopia
Information security professionals struggle to manage all the aspects needed to create effective policies and processes without external partners