
Top 5 Security Considerations for a New Web App
Given the criticality of web application security, it’s imperative to delve deeper into what exactly it entails.
Understanding Server-Side Template Injection (SSTI)
Discover the risks of Server-Side Template Injection (SSTI) vulnerabilities, learn how to detect and prevent them, and safeguard your web applications.
Introducing BILE – Groundbreaking Classification for Web App
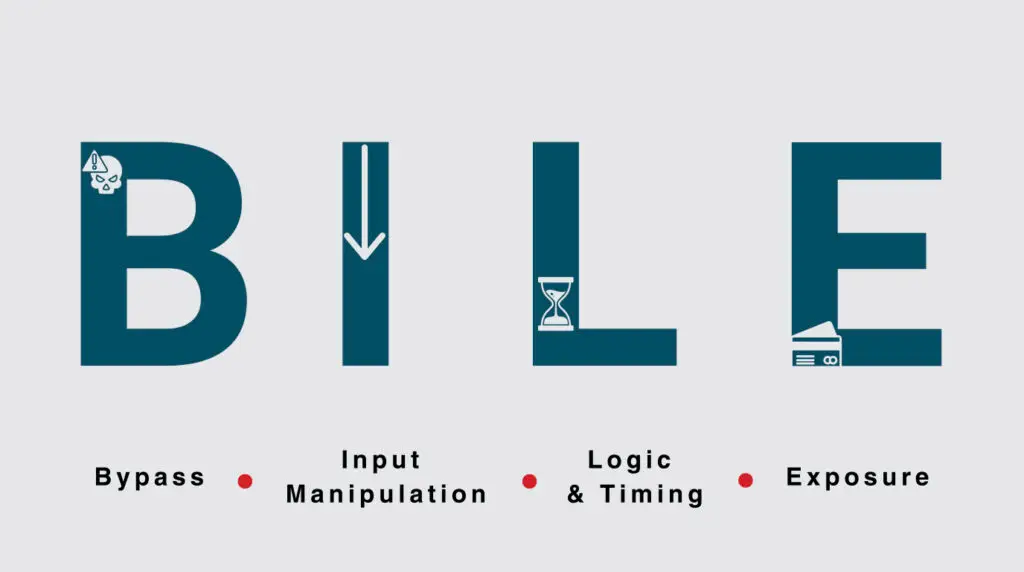
Discover the BILE Classification Scheme, a simple yet effective system for classifying web application vulnerabilities. Download the whitepaper now.
How often should web penetration testing be conducted?
Regular web application penetration testing is crucial for security. Learn how often to conduct tests and tips for effective implementation.
ZAPmas Feedback
A great introduction to ZAP that provide a very fair and balanced comparison to Burp Suite.
12 Days of ZAPmas – Day 12 Testing a new Content-Security-Policy
This final day closes out the series with a look at using ZAP to test and refine a Content-Security-Policy (without breaking your app).
Twelve Days of ZAPmas – Day 11 – ZAP impressions from a Burp user
Day 11 of the series makes a comparison of ZAP versus Burp from the perspective of a long-time Burp user who is relatively new to ZAP.
Twelve Days of ZAPmas – Day 10 – Manual Web App Testing Unproxied
Day 10 of the series delves into manual testing of web apps that you can’t proxy for some reason, and how to work around that limitation.
Twelve Days of ZAPmas – Day 8 – Spidering
Day 8 of the series looks at ZAP’s spidering capabilities and the basic setup for associating login and credentials to a context.
Twelve Days of ZAPMAS – Day 6 – Passive Flaw Detection and Using the HUD
Day 6 of the series looks at ZAP’s use of passive detection rules to identify problems, and it’s injectable head’s up display (HUD).