
Twelve Days of ZAPmas – Day 5 – Scope and Contexts
Day 5 of the series goes over the use of ZAP’s contexts and scope specifier to keep your attacks in-scope.
Twelve Days of ZAPmas – Day 4 – Fuzzing for Injection
The fourth day of the series introduces using ZAP’s Fuzzer tool to fuzz for injection flaws in the client (XSS) and server.
Twelve Days of ZAPmas – Day 3 – CYA (Cover Your Auth)
The third entry in the Twelve Days of ZAPmas series deals with using Zed Attack Proxy’s request tampering to check if your authorization controls work.
Twelve Days of ZAPmas – Day 2 – The Edge of Tomorrow
This second post in the 12 day series uses OWASP Zed Attack Proxy to modify and replay traffic we captured on day 1.
Twelve Days of ZAPmas – Day 1 – Setting Up ZAP
This post kicks off the 12 day series by setting up OWASP Zed Attack Proxy and walks through the manual steps to setup Chrome or Firefox to proxy through.
4 Steps to prepare your application for a Denial of Service attack

How to prepare an application to defend against denial of service (DoS) attacks.
Coming Soon – Twelve Days of ZAPmas
This announcement teases the upcoming (December 2022) series providing an onramp for developers and QA specialists to start using OWASP Zed Attack Proxy.
Quick Bites Ep 4 – Let’s Talk About SSRF, Baby!
This Quick Bites will help you gain a basic understanding of SSRF, how it’s exploited, and how to mitigate it.
Ensuring Web Security via Ansible (Apache)
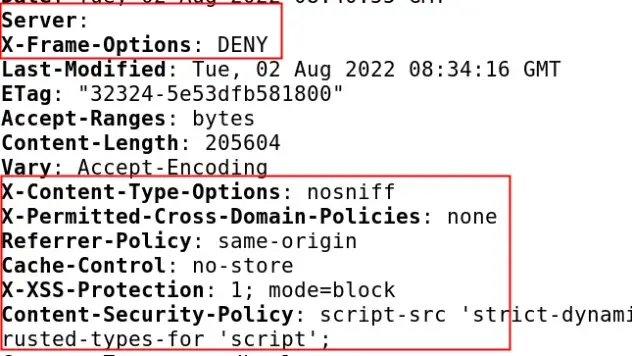
Using ansible to add security headers to an apache web server (idea), environment defined in a Vagrantfile
Why your application needs a Content Security Policy (And How to Build One)
This post outlines the importance of building a content security policy (CSP) to secure web applications, and how to get started building one.