PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Compiling is Not Hiding: Hardcoded Secrets in Mobile Apps

Most of the secrets I’ve found in mobile apps were not stolen. They were shipped. What do I mean by that? I mean nobody needs to break into the vault when the combination is printed on every door. Compiling is not hiding: it changes the format of the code, not...

All Entries

Twelve Days of ZAPMAS Day 6 Passive Flaw Detection and Using the HUD

Twelve Days of ZAPMAS – Day 6 – Passive Flaw Detection and Using the HUD

Day 6 of the series looks at ZAP's use of passive detection rules to identify problems, and it's injectable head's up display (HUD)....
Twelve Days of ZAPmas Day 4 Fuzzing for Injection

Twelve Days of ZAPmas – Day 4 – Fuzzing for Injection

The fourth day of the series introduces using ZAP's Fuzzer tool to fuzz for injection flaws in the client (XSS) and server....
Twelve Days of ZAPmas Day 3 CYA (Cover Your Auth)

Twelve Days of ZAPmas – Day 3 – CYA (Cover Your Auth)

The third entry in the Twelve Days of ZAPmas series deals with using Zed Attack Proxy's request tampering to check if your authorization controls work....
Twelve Days of ZAPmas Day 2 The Edge of Tomorrow

Twelve Days of ZAPmas – Day 2 – The Edge of Tomorrow

This second post in the 12 day series uses OWASP Zed Attack Proxy to modify and replay traffic we captured on day 1....
Twelve Days of ZAPmas Day 1 Setting Up ZAP

Twelve Days of ZAPmas – Day 1 – Setting Up ZAP

This post kicks off the 12 day series by setting up OWASP Zed Attack Proxy and walks through the manual steps to setup Chrome or...
Quick Bites

Quick Bites Ep 6 – Good Hygiene is IMPORTANT, PEOPLE!

Hygiene is an idea most people think they know pretty well. In this Quick Bites, we're going to discuss Cyber Hygiene, and some steps to...
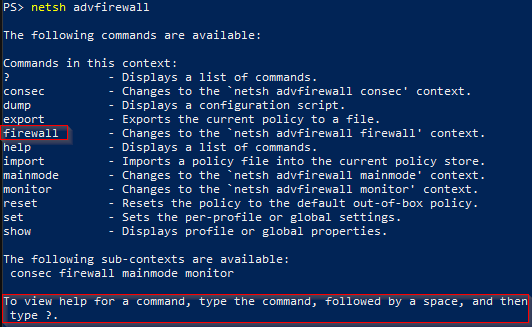
How to iterate through advfirewall rules

How to iterate through advfirewall rules

This article describes how to use Powershell to sort through Windows advfirewall rules and settings such as loops, variable creation, and searching....
default

Introduction to Writing Nmap Scripting Engine (NSE) Scripts

A post that covers the architecture of Nmap's NSE system and the structure of an NSE script....
Quick Bites

Quick Bites Ep 5 – The Call Is Coming From INSIDE THE HOUSE

Let's dive into some horror movies for Halloween! Covering insider threats with the concepts of least-privileges and limitation of responsibilities. Scary!...
Working With Data: IP and Port Filtering

Working With Data: IP and Port Filtering

This article describes how to improve filtering on excel columns containing IP:Port information....
default

4 Steps to prepare your application for a Denial of Service attack

How to prepare an application to defend against denial of service (DoS) attacks....
Coming Soon Twelve Days of ZAPmas

Coming Soon – Twelve Days of ZAPmas

This announcement teases the upcoming (December 2022) series providing an onramp for developers and QA specialists to start using OWASP Zed Attack Proxy....

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy