PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Compiling is Not Hiding: Hardcoded Secrets in Mobile Apps

Most of the secrets I’ve found in mobile apps were not stolen. They were shipped. What do I mean by that? I mean nobody needs to break into the vault when the combination is printed on every door. Compiling is not hiding: it changes the format of the code, not...

All Entries

How to allow multiple RDP sessions

How to allow multiple RDP sessions

Quick technology tips and tricks article to explain how to allow multiple RDP sessions on a Windows machine....
Hunting Secrets

Hunting Secrets

A rundown of the Secrets Hunter capability within Paramalyzer, used to quickly find instances of sensitive information leakage in web applications....
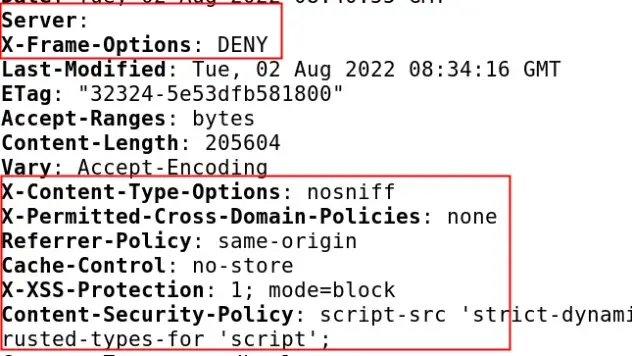
Ensuring Web Security via Ansible (Apache)

Ensuring Web Security via Ansible (Apache)

Using ansible to add security headers to an apache web server (idea), environment defined in a Vagrantfile...
Application Security 101

Application Security 101

Application security is a big job, for sure. And it’s not just the job of the developers or the SOC. There is an incredible amount...
Why your application needs a Content Security

Why your application needs a Content Security Policy (And How to Build One)

This post outlines the importance of building a content security policy (CSP) to secure web applications, and how to get started building one....
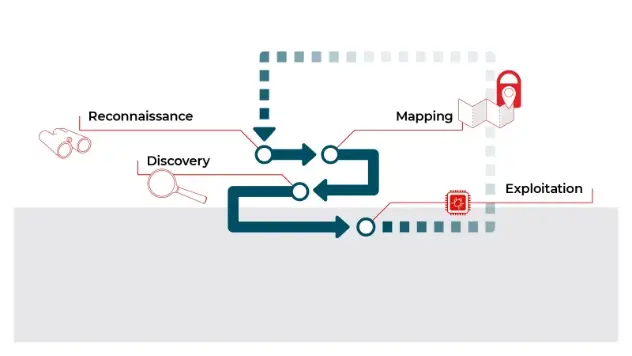
Secure Ideas' Penetration Testing Methodology

Secure Ideas’ Penetration Testing Methodology

This page provides an in depth explanation of our testing methodology as well as a link to download a copy for your reference...
Project Responsibilities

Project Responsibilities

This page details the responsibilities for a project...
sets si apart

What Sets Secure Ideas Apart From Other Security Consulting Firms?

This page outlines Secure Ideas' experience and expertise in the field of information security...
Quick Bites

Quick Bites Episode 2 – HTTP Security Headers and Why You NEED Them

Secure Ideas' Quick Bites Ep 2 - HTTP security headers are important for webapp security. Here are some that will help lockdown your site a...
Privilege Escalation via File

Privilege Escalation via File Descriptors in Privileged Binaries

Post on SetUID drop-privileges binaries with leaked file descriptors, allowing for PrivEsc. Covers how to exploit & a tool to streamline exploitation....
GLBA Safeguards Rule

How to Update the Nmap OUI Database

A blog post on how to update the nmap-mac-prefixes file to improve nmap's OUI detection and provides a script to help streamline the process....
Of MAC Addresses and OUI

Of MAC Addresses and OUI: A Subtle, but Useful, Recon Resource

Blog post explaining how-to extract the OUI information from a MAC address and lookup the manufacture using public data from the IEEE....

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy