PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Compiling is Not Hiding: Hardcoded Secrets in Mobile Apps

Most of the secrets I’ve found in mobile apps were not stolen. They were shipped. What do I mean by that? I mean nobody needs to break into the vault when the combination is printed on every door. Compiling is not hiding: it changes the format of the code, not...

All Entries

Nmap vs. Masscan

Nmap vs. Masscan

A blog comparing the difference between Nmap and Masscan with a use case demonstrating selecting the right tool for the job....
What Tasks are Performed During a Hardware Security Assessment

What Tasks are Performed During a Hardware Security Assessment?

The knowledge base article covers what you can expect when requesting a security assessment of an IoT or embedded device....
Quick Bites

Quick Bites Ep 4 – Let’s Talk About SSRF, Baby!

This Quick Bites will help you gain a basic understanding of SSRF, how it's exploited, and how to mitigate it....
default

How is Embedded/IoT Scoping Different from a Normal Pentest?

An article outlining some things you may want to think about when they are considering a test of an embedded or IoT device due to...
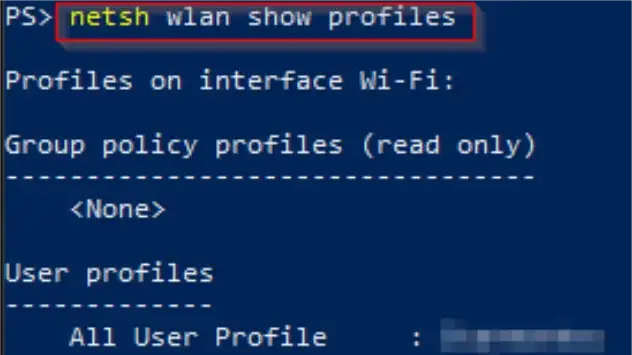
View Wireless Profile Password Information Using PowerShell or CMD

View Wireless Profile Password Information Using PowerShell or CMD

This article describes how to view wireless profiles on a Windows device and to display the password if it’s available....
GLBA Safeguards Rule

What are the key requirements of the GLBA Safeguards Rule?

A walkthrough of the details surrounding the GLBA Safeguards Rule and the main components required for your information security program....
default

Penetration Testing Compliance under GLBA in 2024 – What You Need to Know

This article explains regulatory changes under GLBA in 2024 and how to maintain compliance with penetration testing....
JuiceShop Workshop

JuiceShop Workshop in less than 5 minutes

Have you ever deployed 10-30 containers in AWS with the single stroke of a key? Keep reading to find out how we did exactly this...
How to Obfuscate Strings in Rust the Easy Way Using the litcrypt Crate

How to Obfuscate Strings in Rust the Easy Way Using the litcrypt Crate

How to accomplish string obfuscation in Rust the easy way using the litcrypt crate....
default

Application Security 202: Vulnerabilities Accepted

Studying how to accept vulnerabilities and secure applications...
How Soon Can We Schedule a Test

How Soon Can We Schedule a Test?

This article explains when a test can be scheduled and tips for avoiding project delays...
Quick Bites

(Not So) Quick Bites – Episode 3 – Writing About Writer’s Block

On this (Not So) Quick Bites, we're talking about writer's block, and how to get over it. Here's five tips and tricks that I use...

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy