PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Password Vampires: Don’t Get Bitten Twice

With Halloween right around the corner, let’s talk about your dark secret from the distant past that could really come back to haunt you: that password you’ve been using since 2015. Don’t lie… You know the one.

...

All Entries

default

The ABC’s of ASV’s & PCI

Secure Ideas’ prides itself on providing the highest level of service to our customers. We are tirelessly searching for new tools, and methods to use......
default

Logging Like a Lumber Jack

Turn on any news outlet or visit any news site and you will most likely see an announcement of yet another data breach....
default

Policy Gap Analysis: Filling the Gaps

In the business world there are policies that define how employees should present themselves as well as how company equipment can be used....
default

New Data Security Breach Laws in Florida

Many organizations are collecting what many would consider personal, non-public, information, it is very important that they protect this information....
default

What Do You Expect From A PenTest?

There are many reasons that a company has a penetration test performed. Due to regulatory compliance, like HIPAA, or they are just take security seriously...
default

Comprehensive Testing: Red and Blue Make Purple Webcast

James Jardine and I held the Comprehensive Testing (Purple Teaming) webcast yesterday....
default

Purple Teaming for Success

You know what blue teams and red teams are. Red is our attack side, or the adversaries, and Blue is the defense side....
default

Oversharing: Who Has Access?

What types of information do you copy to a shared folder? Who has access to the share? This can be a difficult problem within many...
default

Is My Application Illegal?

Mobile devices and applications are everywhere, and we have seen tons of guides and what not on how to build successful businesses....
default

Decoding Security Jargon

Just about any security textbook will begin by describing security using terms such as threats, risks, vulnerabilities, exposures, agents, and so on....
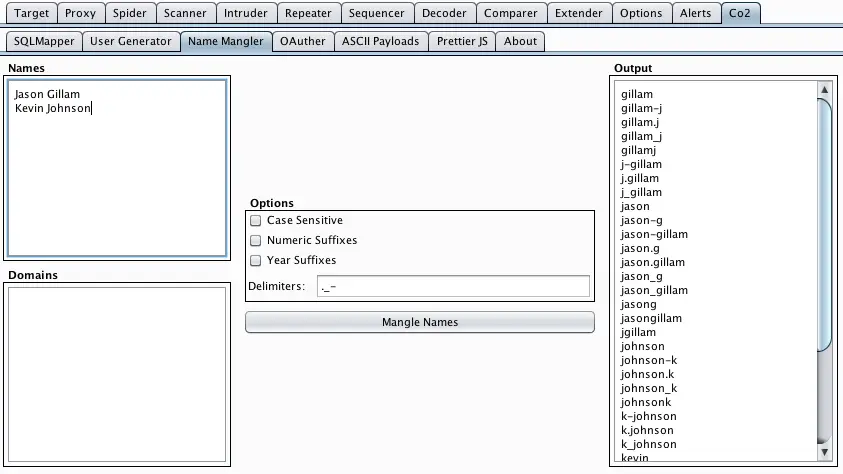
Burp Co2 Update v0.5 adds a Name Mangler module!

Burp Co2 Update v0.5 adds a Name Mangler module!

I’m excited to announce another addition to the Burp Co2 extension bundle in v0.5 of Burp Co2 (download)...
default

Are we a Target?

We entered the year with a slew of privacy events starting with Target’s massive breach, followed by other retailers......

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy.