PROFESSIONALLY EVIL BLOG

We Break Things For a Living.

We Also Write About Things.

Our expert-led content ranges from deep-dives into penetration testing to explorations of hardware hacking. In this digital playground, we unravel the complex world of information security with a touch of fun. Whether you’re curious about Secure Ideas or passionate about cybersecurity, this blog is your quick, enlightening, and entertaining guide into the captivating world of information security. 

Professional Insights Blog

Latest Post

Password Vampires: Don’t Get Bitten Twice

With Halloween right around the corner, let’s talk about your dark secret from the distant past that could really come back to haunt you: that password you’ve been using since 2015. Don’t lie… You know the one.

...

All Entries

default

Introduction to Metasploit Webcast

Whether you’re goal is to become a commercial penetration tester, to demonstrate the risk of a vulnerability, or just need to identify certain weaknesses.....
default

Introducing Burp Correlator!

This new Burp extension is designed to help with efficiency when you are testing a complex application full of parameters or a series of applications....
default

Practical Pentest Advice from PCI

The PCI Security Standards Council released a Penetration Testing Guidance information supplement in March 2015....
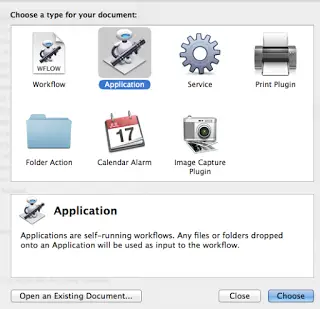
Tip: Running BurpSuite on a Mac

Tip: Running BurpSuite on a Mac

Quick tip to save some time when spinning up Burp Suite on a Mac. Use Burp Suite frequently enough that having an icon on my...
default

Patching binaries with Backdoor Factory

Downloaded binary files from the Internet or grabbed one off of a network share that is used by your organization to store commonly used software?...
default

Don’t Forget the Little Things!

On January 31st, Deusen disclosed what was described as a Same Origin Policy Bypass flaw called “Universal XSS” in IE 9 through 11 on Full...
default

Adventures in LDAP Injection: Exploiting and Fixing

Every pen tester looks forward to that next encounter that includes one of those uncommon vulnerabilities....
default

SamuraiWTF 3.0 and into the future!

We are really excited to announce that SamuraiWTF 3.0 is now available publicly....
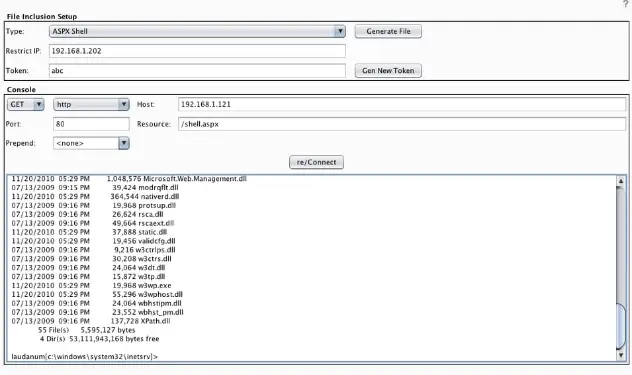
Burp CO2 now sports some Laudanum Scripts!

Burp CO2 now sports some Laudanum Scripts!

Updates to the Burp CO2 extension suite over the past couple of months but the most exciting one is the addition of Laudanum functionality....
default

SQLite: the good, the bad, the embedded database

SQLite is an embedded, open-source, lightweight SQL database engine. The C based library is transactional, self-contained, and highly compact....
phys2

Thumb Drives.. Can you tell the difference?

During a physical penetration test, it is not uncommon for the tester to drop usb thumb drives out in the parking lot or someplace within...
default

CORS Global Policy

I recently noticed an uptake on Cross-Origin Resource Sharing (CORS) findings showing up in automated scanning tools......

Get the Debrief in Your Inbox

New findings, series updates, and usually some bad puns. Delivered when we actually have something worth saying.

No spam. Unsubscribe whenever. We’re evil, not rude.

This website uses cookies

We use cookies to personalize content, provide social media features, and analyze our traffic. We also share information about your use of our site with our analytics partners. You can change your preferences at any time. For more information, please see our Privacy Policy.